Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- What Engineering Performance Testing Should Cover During a Specification ReviewEngineering performance testing for specification review: learn how to verify structural strength, durability, safety, sustainability, and system reliability before costly project decisions.
- Planning Recreational Cable Transport Networks for Resorts and Mountain ParksExplore recreational cable transport networks for resorts and mountain parks, with expert planning insights on capacity, terrain, safety, station design, and long-term performance.
- How to Plan Theme Park Infrastructure for Mixed-Use DevelopmentsTheme park infrastructure for mixed use developments: plan resilient utilities, circulation, attractions, hospitality, and digital systems for scalable destinations.
Popular Tags
TerraVista Metrics (TVM)Industry NewsNetwork Security Risk Assessment for SMEs: Common Gaps and Practical Fixes
auth.Time
Sep 03, 2026Click Count
Why network security becomes a business issue long before a breach appears
Network security usually fails quietly first. Systems still run, guests still check in, and data still moves, yet risk keeps building in the background.
For smaller businesses, the real problem is rarely one dramatic weakness. It is a chain of small gaps across devices, remote access, vendor tools, and old infrastructure.
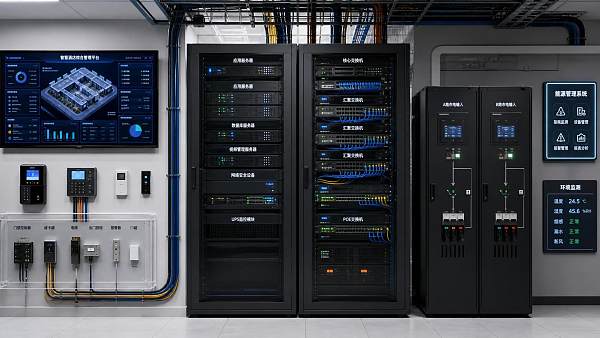
That matters even more in tourism-linked operations, where digital services now sit beside physical assets. A smart hotel network, a modular site office, or an attraction control room all depend on stable network security.
TVM’s broader work around technical benchmarking and operational resilience reflects the same reality. Engineering quality and digital trust need to be tested together, not as separate decisions.
In practice, network security supports uptime, guest confidence, regulatory alignment, and long-term asset performance. That is why risk assessment should follow actual operating conditions rather than generic checklists.
Different operating environments create different network security priorities
Not every site faces the same exposure. A back-office network with limited traffic behaves very differently from a property with guest Wi-Fi, IoT locks, cameras, and third-party cloud platforms.
More connected environments usually create wider attack surfaces. The challenge is not only external intrusion, but also misconfigured devices, shared credentials, and weak segmentation between critical systems.
This is where many SMEs misjudge network security. They assume similar facilities need similar controls, even when occupancy patterns, device density, and vendor dependencies are completely different.
A practical assessment starts with three questions: what must stay available, what data is most sensitive, and which connections are hardest to verify.
A quick view of how risk shifts by setting
Guest connectivity and smart building systems often hide the biggest gaps
In digitally enabled hospitality settings, convenience drives design decisions. Fast onboarding, mobile access, room automation, and integrated booking systems all improve the experience, but they also multiply trust points.
A common network security weakness is placing too much confidence in vendor defaults. Devices arrive preconfigured, dashboards look polished, and connectivity appears stable, so deeper review never happens.
The better approach is to verify how guest traffic, staff devices, smart room controls, and payment systems interact. If those paths overlap too freely, one compromised endpoint can spread disruption quickly.
This is especially relevant for TVM-aligned smart hotel systems, where performance benchmarking should include security protocols and interoperability limits, not only throughput or feature lists.
- Separate guest Wi-Fi from property management, payment, and building automation networks.
- Replace default passwords and disable unused services on connected room devices.
- Require multi-factor authentication for remote dashboards and admin accounts.
- Review whether cloud integrations store logs, credentials, or personal data externally.
Remote sites and modular assets need resilience, not just connectivity
Remote cabins, glamping units, field offices, and temporary tourism infrastructure create a different network security profile. The issue is often limited visibility rather than high traffic volume.
These sites may rely on consumer-grade routers, shared maintenance accounts, or delayed firmware updates. If a device fails or is exploited, local teams may not even notice immediately.
In actual use, strong network security here means designing for low-touch maintenance. Controls must work even when on-site technical support is limited and equipment replacement takes time.
That makes lifecycle discipline important. A well-built eco-structure can still become a weak point if its connected monitoring hardware remains unsupported after deployment.
Practical fixes include maintaining an asset register, defining patch responsibility in service contracts, and restricting remote administration to approved devices and scheduled windows.
Vendor access is where many SMEs underestimate network security risk
Third-party support is now built into most operating models. Surveillance platforms, HVAC controls, booking software, amusement systems, and payment tools all bring external connections into the network.
The mistake is assuming reputable vendors automatically reduce risk. In reality, every remote support path becomes part of the network security boundary.
Some vendors need frequent access. Others only need emergency maintenance. Those differences matter because controls should reflect actual use rather than broad permanent privileges.
What to verify before approving external access
- Whether access is always on or enabled only when needed.
- Whether vendor accounts are unique, logged, and protected by multi-factor authentication.
- Whether data flows cross borders or enter subcontractor systems.
- Whether software updates are tested before deployment on live operations.
This is one area where technical due diligence and procurement intelligence should connect. Contract terms, serviceability, and compliance posture all shape the practical strength of network security.
The most common misjudgments are operational, not technical
Many weaknesses remain because they do not look urgent. An old switch still works. A shared admin account seems convenient. A camera network appears separate, but actually routes through the same core path.
In broader tourism environments, the pressure to keep experiences seamless can push security review behind rollout speed. That is understandable, but it creates hidden fragility.
The more useful judgment is not asking whether a system is modern. It is asking whether its real dependencies are documented, limited, and recoverable.
- Do not judge network security only by firewall presence. Review identity, segmentation, and monitoring together.
- Do not treat similar sites as identical if occupancy, vendor mix, or device counts differ.
- Do not compare solutions only by acquisition cost. Maintenance effort and patch discipline affect total risk.
- Do not ignore unsupported hardware simply because replacement is inconvenient.
A practical assessment model works better than a theoretical one
For most SMEs, the best network security assessment is not the most complex. It is the one tied closely to actual assets, service dependencies, and realistic failure scenarios.
Start by mapping critical systems. Include internet links, wireless networks, IoT devices, operational technology, cloud tools, and all remote support channels.
Then rank them by business impact. Focus first on systems that affect guest data, payments, access control, safety monitoring, or operational uptime.
After that, test whether current controls match the environment. Some sites need stronger segmentation. Others need better visibility, faster patching, or stricter vendor governance.
Priority actions that usually produce immediate value
What to do next if network security review has been delayed
Begin with the environments where digital service quality and operational continuity meet. Those points usually reveal the most meaningful network security gaps first.
Document which systems carry sensitive data, which devices depend on outside vendors, and which assets cannot tolerate downtime. That creates a usable risk map.
From there, compare site conditions rather than applying one uniform rule. A smart property, a remote eco-site, and an attraction control network should not be judged by the same assumptions.
The strongest network security decisions usually come from combining technical review with operational context. That is also how resilience becomes measurable, maintainable, and easier to scale.
A practical next step is to set a simple assessment standard for segmentation, access control, vendor paths, patch status, and recovery readiness across every connected location.
Recommended News
 Sep 05, 2026What Engineering Performance Testing Should Cover During a Specification ReviewEngineering performance testing for specification review: learn how to verify structural strength, durability, safety, sustainability, and system reliability before costly project decisions.
 Aug 11, 2026How to Evaluate Materials Performance Analysis Services in Europe for Compliance-Critical ProjectsMaterials performance analysis Europe: learn how to compare accredited labs, verify compliance readiness, and choose a provider whose data, methods, and reports stand up to real project scrutiny.
 Jul 27, 2026Product Application Analysis for Procurement: How to Compare Fit, Risk, and ROIProduct application analysis for procurement helps buyers compare fit, compliance risk, lifecycle cost, and ROI with confidence. Learn a practical framework to avoid costly sourcing mistakes.
 Jul 22, 2026How to Evaluate Weather Resistance in Materials Performance Analysis?Materials performance analysis weather resistance explained: learn how to assess UV, moisture, temperature, and corrosion risks to choose durable materials with confidence.
 Jul 15, 2026Cloud Storage for Business: How to Compare Security, Access Speed, and Backup CostsCloud storage for business: compare security, access speed, and backup costs with a practical framework to reduce risk, control spend, and choose the right provider with confidence.
 Jul 14, 2026What Are Standardized Performance Benchmarks Ratings Used For in Vendor Evaluation?Standardized performance benchmarks rating explains how buyers compare vendors with verified data on compliance, durability, and lifecycle value for smarter procurement decisions.
 Jul 13, 2026Product Benchmarking Rating Explained: How to Compare Scores Across SuppliersProduct benchmarking rating explained: learn how to compare supplier scores with confidence, verify methodology, spot hidden risks, and make smarter procurement decisions.
 Jul 13, 2026How to Choose a Product Benchmarking Data Provider for Reliable Market ComparisonsProduct benchmarking data provider selection starts with methodology, transparency, and sector fit. Learn how to compare providers for reliable market insights and smarter procurement decisions.
 Jul 10, 2026Technical Integration Resilience Explained: How to Reduce Downtime Across Connected SystemsTechnical integration resilience explained: learn how to reduce downtime, prevent cascading failures, and improve uptime across connected systems with practical planning insights.
 Jul 08, 2026How to Use Product Benchmarking KPIs to Compare Competing SolutionsProduct benchmarking KPIs help you compare competing solutions with real evidence. Learn how to measure performance, lifecycle cost, compliance, and risk for smarter buying decisions.
 Jul 05, 2026How to Run an Environmental Sustainability Assessment: Metrics, Boundaries, and Trend AnalysisEnvironmental sustainability assessment trend analysis made practical: learn how to set metrics and boundaries, compare lifecycle impacts, and turn sustainability data into smarter decisions.
 Jul 04, 2026Hospitality Design Benchmarks Metrics Explained: Which KPIs Matter for Guestroom Upgrades?Hospitality design benchmarks metrics explained: discover the KPIs that matter most for guestroom upgrades, from lifecycle cost and durability to energy use, maintenance, and guest satisfaction.
 Jul 02, 2026How to Compare Product Category Pricing Models for Better Margin PlanningProduct category pricing model comparison made practical: learn how to evaluate total cost, hidden risks, and lifecycle value to improve margin planning and make smarter sourcing decisions.
 Jun 30, 2026How Technical Explainer Content for Procurement Helps Compare Specs, Risks, and SuppliersTechnical explainer content for procurement helps teams compare specs, uncover supplier risks, and choose solutions that improve compliance, lifecycle value, and long-term performance.
 Jun 29, 2026System Interoperability Testing Vendors: Key Criteria for Compliance and PerformanceSystem interoperability testing vendors compared: discover how to assess compliance, performance, independence, and real-world reliability before costly integration failures happen.
 Jun 28, 2026Product Benchmarking Explained: How to Compare Performance, Cost, and QualityProduct benchmarking explained: learn how to compare performance, cost, and quality with a practical framework that reduces risk, improves supplier selection, and supports smarter long-term decisions.
 Jun 27, 2026How to Build a Product Benchmarking Comparison Matrix for Hospitality Equipment SelectionProduct benchmarking comparison matrix guide for hospitality equipment selection. Learn to compare cost, compliance, durability, and lifecycle value with confidence.
 Jun 25, 2026What Drives System Interoperability Testing Implementation Cost in Multi-Vendor Projects?System interoperability testing implementation cost rises in multi-vendor projects due to scope gaps, retesting, compliance, and downtime risk. Learn how to control costs early.
 Jun 24, 2026Maintenance Planning Workflow Automation: Which Tasks Should You Automate First?Maintenance planning workflow automation starts with the right tasks. Learn what to automate first to cut downtime, improve data quality, and boost asset performance.
 Jun 22, 2026How Data-Backed Procurement Helps Compare Vendors and Control Purchasing RiskData-backed procurement helps buyers compare vendors with verified performance, lifecycle cost, and compliance data to reduce purchasing risk and make smarter, safer decisions.
 Jun 21, 2026Product Selection Criteria: How to Compare Performance, Cost, and Fit for UseProduct selection criteria made practical: learn how to compare performance, life-cycle cost, compliance, and fit for use to make smarter, lower-risk asset decisions.
 Jun 20, 2026Virtual Learning for Staff Training: When It Works Best and Where It Falls ShortVirtual learning works best for scalable knowledge transfer, compliance, and systems training. Discover where it delivers ROI, where it falls short, and how to choose the right staff training mix.
 Jun 19, 2026Thermal Efficiency Testing U Value: What It Means for Wall and Window SelectionThermal efficiency testing U value explained: learn how to compare walls and windows with verified data to cut energy costs, improve comfort, and make smarter project decisions.
 Jun 16, 2026How to Choose an LMS for Employee Training: Features, Integrations, and Reporting NeedsLMS selection starts with fit, integrations, and reporting. Learn how to choose an LMS for employee training that improves compliance, scales operations, and delivers measurable performance.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.