Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- How to Use Practical Industry Reports to Identify Market Risks and Growth OpportunitiesPractical industry reports help uncover market risks, validate supplier claims, and identify growth opportunities before capital is committed.
- Cloud Integration Interoperability Testing: Methods, Metrics, and Release GatesSystem interoperability testing cloud integration: explore practical methods, key metrics, and evidence-based release gates for secure, reliable connected operations.
- Hotel Security Protocols: A Compliance Checklist for Protecting Guests and StaffSecurity protocols for hospitality: use this practical hotel compliance checklist to protect guests, staff, data, access points, and emergency operations.
Popular Tags
TerraVista Metrics (TVM)Industry NewsCyber security for B2B gets expensive when access rules stay outdated
auth.Time
Sep 11, 2026Click Count
Cyber security for B2B becomes a costly weakness when outdated access rules fail to match today’s connected operations. For quality control and security managers in tourism infrastructure and smart hospitality projects, poor permission design can expose sensitive data, disrupt integrated systems, and increase compliance risk. This article explores why modern access governance is now essential for protecting performance, trust, and long-term procurement value.
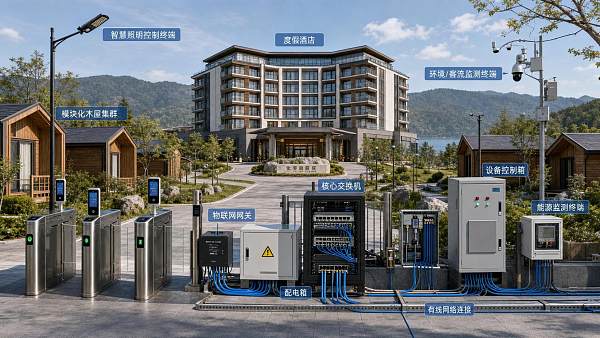
In tourism and hospitality infrastructure, access control is no longer limited to office logins. It now affects IoT gateways, smart room systems, environmental controls, procurement dashboards, engineering documentation, supplier portals, and maintenance records. When these systems are connected across 3 to 7 operational layers, a single outdated rule can allow the wrong person to view, change, export, or disable critical data.
For organizations working with prefab glamping units, hotel AI platforms, amusement hardware, and carbon-compliance reporting, Cyber security for B2B is directly tied to quality assurance and long-term asset performance. Security managers and QC teams increasingly need access models that reflect real workflows, vendor involvement, maintenance cycles, and cross-border procurement requirements rather than legacy IT assumptions from 5 or 10 years ago.
Why outdated access rules create high-cost risk in smart tourism infrastructure
Legacy permission structures were built for simpler environments: a small number of users, a limited on-premise network, and clear department boundaries. Modern tourism assets operate very differently. A single resort, eco-lodge cluster, or smart hotel project can involve 20 to 50 external contributors during design, installation, calibration, handover, and ongoing service support.
When access policies are not updated, the first problem is over-permission. Engineers may keep administrator rights after commissioning. Vendors may retain remote access beyond the 30-day support window. Procurement teams may view technical test archives they do not need, while QC staff may be unable to approve firmware changes fast enough. This mismatch slows operations and expands the attack surface at the same time.
The second problem is under-controlled system interaction. In smart hospitality projects, room automation, HVAC controls, metering, occupancy sensors, and property management integrations often exchange data every few seconds or minutes. If role design does not distinguish between read-only, diagnostic, configuration, and override privileges, a routine maintenance action can become an operational incident within 15 minutes.
Where the exposure usually appears
Cyber security for B2B failures linked to outdated access rules often emerge in predictable locations. These weak points are especially common when organizations focus on hardware quality but postpone digital governance until late-stage delivery.
- Shared maintenance accounts used by 3 to 12 technicians across multiple sites
- Supplier portals with no expiry date for document downloads or API keys
- IoT dashboards where monitoring users also have parameter editing rights
- Temporary commissioning access that remains active after handover
- Carbon and sustainability reporting files stored in broad-access folders
- Remote support channels without session logging or approval checkpoints
For TerraVista Metrics, this matters because infrastructure benchmarking is only as credible as the integrity of the underlying data. Thermal performance records, network throughput logs, and material fatigue reports lose decision value when access history is unclear or when datasets can be altered without traceable authorization.
Operational impact for quality and security managers
Quality teams are often measured on consistency, traceability, and acceptance accuracy. Security teams are measured on protection, continuity, and incident response. Outdated access rules undermine both. A failed segregation model can increase verification time by 20% to 40% because teams must manually confirm who changed settings, who approved them, and whether the change was expected.
In procurement-heavy projects, this can also trigger disputes. If sensor calibration values, cabin insulation test files, or amusement equipment maintenance logs are modified after review, vendor accountability becomes harder to establish. The result is more reinspection, longer acceptance cycles, and higher legal or insurance exposure.
The table below outlines common outdated access patterns and the practical costs they create in tourism infrastructure environments.
The main lesson is simple: access governance is not an IT formality. In connected tourism operations, it influences uptime, quality validation, supplier control, and revenue readiness. That is why Cyber security for B2B should be reviewed alongside technical durability, carbon compliance, and system integration during procurement and commissioning.
How to design access governance that fits B2B tourism operations
A practical model starts with business roles, not software menus. Security managers should map who needs access, why they need it, how long they need it, and what operational consequence follows if they misuse it. In most hospitality infrastructure projects, 4 core dimensions matter: role, asset type, project phase, and approval level.
For example, a commissioning engineer may require temporary write access for 7 to 14 days, while a QC auditor only needs read-only access with export rights for accepted test files. A sustainability consultant may need monthly reporting access but no ability to change carbon calculation inputs. These distinctions reduce unnecessary permissions without slowing real work.
A four-layer control model
Many organizations improve Cyber security for B2B by using a four-layer control model that can be adapted across hotels, resorts, attraction facilities, and glamping developments.
- Identity layer: named users, no shared credentials, role-linked authentication
- Permission layer: read, diagnose, configure, approve, and override separated clearly
- Time layer: access windows limited by shift, project phase, or support contract period
- Audit layer: logs retained for at least 90 to 180 days depending on system criticality
This model is especially useful when multiple vendors support different systems, such as room automation, smart locks, environmental sensors, and guest-facing AI modules. The goal is not to create friction. It is to ensure that every digital action has a valid business reason and a reviewable trail.
Minimum controls for high-value infrastructure data
Some datasets deserve stricter treatment because they influence procurement, performance verification, and liability. These include acceptance test results, firmware baselines, equipment maintenance histories, energy-efficiency benchmarks, and carbon documentation. Access to these records should include version control, approval logging, and at least 2-person review for deletion or overwrite actions.
The following table shows a practical access design framework for common roles in smart hospitality and tourism infrastructure projects.
This structure helps organizations align security with operational reality. It protects critical systems while keeping approvals fast enough for installation deadlines, acceptance milestones, and maintenance response targets.
Questions to ask during procurement and vendor review
For quality and security leaders, vendor selection should include access governance questions as early as the RFI or technical review stage. If a product is benchmarked for throughput, thermal efficiency, or durability but cannot support role-based permissions, audit logs, or access expiry, the total lifecycle risk may outweigh the initial technical advantage.
- Can the system separate monitor, configure, approve, and admin functions?
- Does remote access support time limits, session records, and approval checkpoints?
- Can logs be exported for 90, 180, or 365 days without manual reconstruction?
- How are supplier accounts removed during handover or contract change?
- Are firmware and configuration changes tied to named users and timestamps?
- Can the platform segment access by building, site, cluster, or asset group?
These questions are highly relevant for TerraVista Metrics users because procurement decisions in tourism infrastructure increasingly depend on measurable, verifiable, and auditable system behavior. Technical beauty without governance discipline creates hidden cost later.
Implementation steps for quality control and security teams
Improving Cyber security for B2B does not always require a full platform replacement. In many projects, the first 30 to 60 days should focus on access mapping, privilege cleanup, and acceptance-rule updates. This delivers faster risk reduction than waiting for a larger digital transformation program.
Step-by-step rollout plan
- Inventory all connected systems, portals, and data repositories used across the asset lifecycle.
- Identify every user category, including contractors, OEM support, auditors, and consultants.
- Classify permissions into at least 4 levels: observe, operate, configure, approve.
- Remove dormant accounts older than 60 or 90 days unless there is a valid exception.
- Set automatic expiry for temporary vendor access and require named-user credentials.
- Review logs monthly for critical systems and quarterly for lower-risk platforms.
This process is most effective when tied to quality checkpoints such as FAT, SAT, commissioning approval, energy validation, and final handover. If access governance is linked to these gates, teams avoid the common problem of technical sign-off without digital control closure.
Common mistakes to avoid
Several mistakes appear repeatedly in tourism projects. One is assuming that network security alone solves access risk. Another is treating vendor trust as a substitute for permission discipline. A third is forgetting that data integrity matters as much as data secrecy when benchmark results influence procurement and performance claims.
QC and security teams should also avoid overcomplicated approval chains. If emergency access takes 6 signatures and 4 hours, staff will create workarounds. A better design uses pre-approved escalation paths, defined time windows such as 2 hours or 12 hours, and automatic revocation when the task ends.
How benchmarking supports better cyber decisions
Infrastructure benchmarking is often associated with physical or performance characteristics, but it can also improve access governance. When teams compare systems using standard criteria such as audit retention, role granularity, remote support controls, and export traceability, Cyber security for B2B becomes part of measurable procurement quality rather than a vague promise.
For a think tank like TerraVista Metrics, this approach is valuable because global buyers need more than marketing claims. They need structured evidence showing whether a smart hospitality product can protect operational continuity over a 3-year, 5-year, or 10-year lifecycle. That is especially important when Chinese manufacturing capability is being evaluated for international deployment and compliance-sensitive projects.
What strong access governance looks like in long-term procurement value
Effective access governance improves more than defense posture. It shortens dispute resolution, reduces rework, strengthens supplier accountability, and helps operators maintain consistent evidence for sustainability, safety, and performance reviews. In practical terms, it protects asset value long after installation is complete.
For procurement directors, a system with clear role controls may be worth a higher initial price if it lowers intervention hours, acceptance delays, and incident recovery effort over the next 24 to 60 months. For QC managers, stronger logging and permission boundaries make technical verification more credible. For security managers, they reduce uncertainty during investigations and contract transitions.
That is why Cyber security for B2B should be evaluated as a procurement-quality factor, not just a post-purchase IT issue. In connected tourism infrastructure, access rules shape the reliability of smart cabins, hotel platforms, IoT networks, and operational data used to support guest experience, energy efficiency, and compliance.
Final takeaway for decision-makers
Outdated access rules create invisible cost until something fails: a vendor account stays active, a benchmark record changes without trace, a live setting is edited by the wrong role, or an audit trail cannot explain a system disruption. By then, the cost is usually much higher than the effort required to modernize permissions earlier.
Organizations that manage smart hospitality, tourism hardware procurement, and infrastructure quality should treat access governance as a core control layer alongside durability testing, integration review, and carbon compliance validation. If you need a more structured way to assess technical systems, benchmark supplier readiness, or identify control gaps in tourism infrastructure projects, contact TerraVista Metrics to get a tailored evaluation framework and learn more solutions built for measurable procurement confidence.
Recommended News
 Sep 11, 2026Hotel Security Protocols: A Compliance Checklist for Protecting Guests and StaffSecurity protocols for hospitality: use this practical hotel compliance checklist to protect guests, staff, data, access points, and emergency operations.
 Sep 03, 2026How to Plan Theme Park Infrastructure for Mixed-Use DevelopmentsTheme park infrastructure for mixed use developments: plan resilient utilities, circulation, attractions, hospitality, and digital systems for scalable destinations.
 Aug 23, 2026What Makes Community Based Eco Resort Development Successful in Rural Destinations?Community based eco resort development succeeds when land fit, local participation, infrastructure, and operations align. Discover practical strategies for resilient, high-value rural eco resorts.
 Aug 21, 2026How Many Rooms Should an Eco Resort Have to Balance ROI and Guest Experience?Eco resort development room count directly shapes ROI, infrastructure efficiency, and guest privacy. Learn how to choose the right key range to protect margins and elevate the experience.
 Aug 15, 2026How to Analyze Stainless Steel Fatigue in Cyclic Load ApplicationsStainless steel fatigue analysis helps you spot hidden cyclic load risks early, improve reliability, and prevent costly failures in real-world applications.
 Aug 08, 2026Hospitality Engineering Standards for Resorts: Key Compliance Checks Before Design ApprovalHospitality engineering standards for resorts explained: discover the key compliance checks before design approval to avoid delays, reduce risk, and build guest-ready, resilient resort projects.
 Jul 21, 2026Tourism Destination Infrastructure Solutions: How to Plan Smarter Visitor FacilitiesTourism destination infrastructure solutions for smarter visitor facilities: learn how to reduce risk, improve uptime, and plan scalable, data-backed destinations that perform long term.
 Jul 19, 2026How to Choose Rustproof Hotel Furniture for Coastal and High-Humidity PropertiesRustproof hotel furniture is essential for coastal and high-humidity properties. Learn how to compare materials, finishes, and supplier claims to reduce maintenance costs and extend service life.
 Jul 16, 2026How to Choose Resort Bar Furniture for Outdoor Hospitality SpacesResort bar furniture buying guide for outdoor hospitality spaces: compare materials, durability, comfort, and maintenance to choose stylish, long-lasting commercial pieces.
 Jul 15, 2026Commercial Thermal Efficiency Testing: Key Metrics, Test Methods, and Compliance BasicsCommercial thermal efficiency testing explained: learn key metrics, test methods, common compliance risks, and practical steps to improve performance, cut costs, and make smarter asset decisions.
 Jul 14, 2026Smart Tourism Integration vs Standalone Systems: Which Setup Fits Multi-Site Operations?Smart tourism integration or standalone systems? Discover which setup best fits multi-site tourism operations, improves visibility, compliance, scalability, and guest experience.
 Jul 13, 2026Export Market Opportunities in Latin America: How to Identify Profitable Entry PointsExport market opportunities in Latin America are shifting toward high-margin, compliant sectors. Discover how to spot profitable entry points in tourism, hospitality, and smart infrastructure.
 Jul 12, 2026Carbon Compliance in North America: Key Reporting Rules and Risk Points for ManufacturersCarbon compliance North America: learn the key U.S. and Canada reporting rules, top risk points for manufacturers, and how to strengthen data, supplier checks, and compliance readiness.
 Jul 11, 2026How to Evaluate Coated Surface Structural Performance Testing for Outdoor InstallationsCoated surface structural performance testing for outdoor installations: learn how to assess adhesion, crack resistance, corrosion durability, and real-world structural risk before procurement.
 Jul 10, 2026Outdoor Furniture Durability Cost: Which Materials Last Longer and Cost Less to Maintain?Outdoor furniture durability cost explained: compare aluminum, teak, steel, and HDPE to find materials that last longer, reduce maintenance, and deliver better long-term value.
 Jul 09, 2026Technical Integration Security: Key Standards, System Architecture, and Risk ChecksTechnical integration security explained: explore key standards, system architecture signals, and risk checks to build resilient, compliant, and scalable connected infrastructure.
 Jul 08, 2026Tourism Asset Evaluation in Middle East: Key Metrics for Hotel and Resort ProjectsTourism asset evaluation in Middle East explained through key metrics for hotel and resort projects, covering location, infrastructure, lifecycle cost, sustainability, and technology.
![]() Jul 07, 2026Eco Building Materials Manufacturer Checklist: Certifications, MOQ, and Custom OptionsEco building materials manufacturer checklist covering certifications, MOQ, and custom options. Learn how to compare suppliers, reduce project risk, and choose sustainable materials with confidence.
 Jul 06, 2026Hospitality Fire Safety Standards Explained: Key Compliance Points for Hotels and ResortsHospitality fire safety standards explained for hotels and resorts: learn key compliance points, risk areas, and practical steps to protect guests, assets, and operations.
 Jul 03, 2026How to Specify High Traffic Furniture Weight Capacity for Hotels, Lobbies, and Public AreasHigh traffic furniture weight capacity for hotels, lobbies, and public areas: learn how to verify load ratings, testing standards, and durability specs to reduce risk and choose smarter.
 Jul 03, 2026Hospitality Procurement Finish Standards Explained: How to Compare Durability, Cost, and ComplianceHospitality procurement finish standards explained: compare durability, lifecycle cost, and compliance with a practical framework for smarter sourcing and fewer costly project delays.
 Jun 30, 2026Tourism Equipment Evaluation Compliance: What to Check Before Purchase and Site DeploymentTourism equipment evaluation compliance: learn what to verify before purchase and site deployment to reduce risk, control costs, ensure safety, and choose suppliers with confidence.
 Jun 28, 2026How to Select Durable Hotel Furniture for Waiting Areas with High Guest TurnoverDurable hotel furniture for waiting areas: learn how to choose seating and surfaces that withstand high guest turnover, reduce maintenance costs, and protect your hotel’s first impression.
 Jun 27, 2026Sustainable Tourism Construction: 7 Design Priorities for Low-Impact Hospitality ProjectsSustainable tourism construction: discover 7 design priorities for low-impact hospitality projects that cut risk, improve lifecycle performance, and boost guest, investor, and ESG value.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.