Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- How to Evaluate Spark Plug Suppliers for Consistent Quality and Lead TimesSpark plugs supplier evaluation guide: compare quality control, traceability, fitment, total cost, and reliable lead times to secure dependable engine maintenance supply.
- What Drives System Interoperability Testing Service Costs in Complex Projects?System interoperability testing service cost depends on integration scope, workflows, environments, and assurance needs. Learn how to budget smarter and reduce project risk.
- Project Planning Sourcing Guides: How to Qualify Suppliers Before Work StartsSourcing guides project planning helps teams qualify suppliers before work begins—verify compliance, delivery capacity, financial strength, and sustainability to reduce risk and protect project outcomes.
Popular Tags
TerraVista Metrics (TVM)Industry NewsHotel Security Protocols: A Compliance Checklist for Protecting Guests and Staff
auth.Time
Oct 07, 2026Click Count
Effective security protocols for hospitality are no longer confined to a guard at the entrance, a camera above the lobby, and a key cabinet behind reception. A hotel’s security posture now extends through guestroom access, outsourced contractors, payment systems, connected devices, emergency communications, staff wellbeing, and the operational decisions made during an ordinary shift.
For quality-control and security managers, the challenge is not simply acquiring more security technology. It is proving that the entire environment works as a coordinated, auditable system. A door lock may meet a technical specification, but the property is still exposed if access credentials are not withdrawn when an employee leaves. A video surveillance platform may be modern, yet create legal and reputational risk if retention periods, viewing permissions, and incident export procedures are unclear.
This checklist is designed as a practical compliance framework for hotel operators, developers, and procurement teams. It can support internal audits, pre-opening reviews, supplier assessments, and improvement plans across full-service hotels, resorts, aparthotels, modular properties, and remote hospitality sites.
Start with a documented security governance model
Security controls tend to fail when responsibility is spread across departments without a clear owner. Front office may manage keys, engineering may administer locks and networked devices, IT may oversee identity systems, and human resources may hold employee records. Each team may be doing its part, but a compliance gap can emerge in the handover between them.
A usable governance model should define who is accountable for security policy, daily implementation, audit verification, incident escalation, and final corrective action. It should also distinguish between hotel-operated functions and third-party responsibilities, particularly where security personnel, valet services, maintenance, laundry, entertainment, or IT support are outsourced.
- Maintain a written security policy approved by senior management and reviewed on a scheduled basis.
- Create a property-specific risk register covering crime, fire, severe weather, crowd management, cyber threats, medical emergencies, and local environmental risks.
- Assign named owners for physical security, data protection, emergency planning, and contractor controls.
- Record compliance duties arising from local laws, fire codes, labor rules, privacy requirements, insurance conditions, and franchise standards.
- Use version-controlled procedures so staff are not relying on outdated printed instructions.
There is no single global hotel security certification that replaces local legal requirements. Compliance must be interpreted by jurisdiction and property type. However, internationally recognized management principles—such as risk-based controls, documented processes, training records, corrective actions, and continual improvement—provide a reliable foundation for benchmarking.
1. Control entry without making the guest experience feel hostile
Guest safety begins well before a room is assigned. The public-facing character of a hotel creates a difficult balance: visitors should feel welcomed, while unauthorized access to guestrooms, staff-only areas, loading bays, back corridors, and plant rooms must be restricted.
During an audit, evaluate the whole access journey rather than inspecting individual doors in isolation. A secure guestroom lock offers limited protection if someone can tailgate through a service entrance, obtain an unattended master credential, or enter an elevator zone without challenge.
Physical access checklist
- Verify that guestroom, staff, contractor, and emergency credentials use distinct access profiles.
- Set procedures for issuing, replacing, auditing, and revoking keycards, mobile keys, mechanical keys, and master credentials.
- Require immediate deactivation of access rights for terminated employees, transferred staff, and completed contractors.
- Review access logs for sensitive areas, including server rooms, cash offices, medication storage, security control rooms, and engineering spaces.
- Inspect exterior doors, parking areas, rooftop access, delivery entrances, perimeter gates, and emergency exits for forced-entry vulnerabilities.
- Confirm that emergency exits allow safe egress while preventing routine unauthorized entry.
- Use visitor and contractor sign-in controls appropriate to the property’s risk profile.
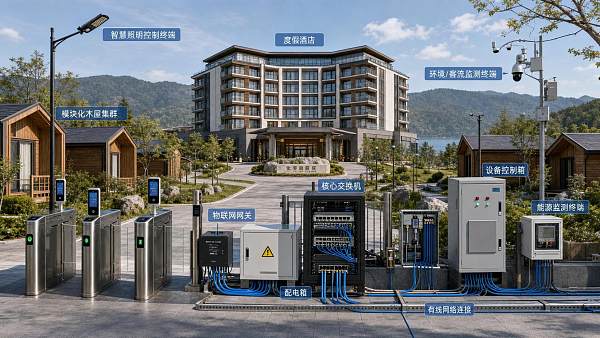
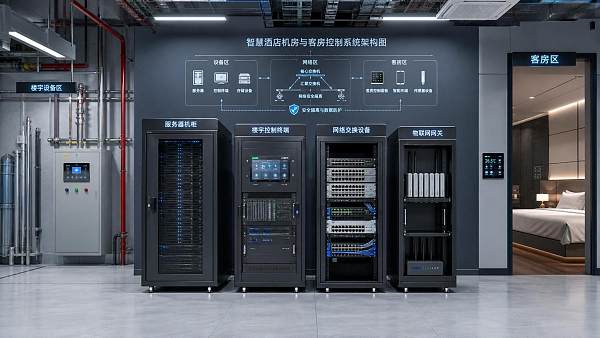
For smart hotel systems, interoperability matters as much as hardware quality. Door locks, elevator controls, property-management systems, staff identity platforms, and incident reporting tools should have defined integration rules. Procurement teams should ask whether access logs can be retained, exported, protected from alteration, and reviewed without relying on a single vendor technician.
2. Treat surveillance as evidence management, not decoration
Cameras can deter opportunistic misconduct and support investigations, but only when their placement, reliability, and governance are properly managed. “Cameras installed” is not a meaningful compliance outcome. The real questions are whether critical areas are covered, whether recordings are usable in realistic lighting conditions, and whether authorized staff can retrieve relevant footage promptly and lawfully.
Coverage should be risk-led. High-priority locations often include entrances, reception, cash handling points, elevators, corridors leading to guestroom areas, parking facilities, loading zones, public recreational areas, and selected back-of-house routes. Cameras should not be installed in private areas such as guestrooms, bathrooms, changing rooms, or other locations where surveillance would violate privacy expectations or legal restrictions.
- Document camera locations, field of view, recording schedules, and blind-spot reviews.
- Test image quality in daylight, low light, glare, and adverse weather where applicable.
- Limit live-view and playback access to authorized roles, with access logs where the system supports them.
- Define retention periods based on applicable privacy law, security needs, and active investigations.
- Securely preserve footage when an incident is reported, avoiding accidental overwrite.
- Post clear surveillance notices where required and maintain a lawful basis for processing personal data.
A recurring mistake is treating video surveillance as the entire security program. Cameras document events; they do not replace trained staff, working locks, visitor controls, or a calm and timely response process.
3. Protect hotel networks, connected rooms, and guest data
Hospitality is increasingly dependent on connected infrastructure. Mobile check-in, smart TVs, in-room tablets, occupancy sensors, digital signage, payment terminals, building-management systems, and AI-supported service platforms can improve operations—but they also widen the attack surface.
Cybersecurity belongs in security protocols for hospitality because a digital disruption can rapidly become a guest safety issue. If access control fails, emergency messaging becomes unavailable, payment systems are compromised, or a building system cannot be managed remotely, the operational consequences extend beyond IT.
Digital security controls to verify
- Separate guest Wi-Fi, corporate systems, payment environments, operational technology, and IoT devices through appropriate network segmentation.
- Maintain an inventory of connected assets, software versions, account owners, and end-of-support dates.
- Apply multi-factor authentication for privileged accounts and remote administration whenever feasible.
- Remove default passwords, restrict vendor remote access, and review access after maintenance work is completed.
- Patch systems under a documented process that considers uptime, compatibility, and security urgency.
- Encrypt sensitive data in transit and at rest where required by the system and applicable regulations.
- Test backup restoration, not merely backup creation, for critical operational and security systems.
Payment data deserves its own control environment. Hotels should work with qualified payment providers and follow the applicable Payment Card Industry Data Security Standard requirements. Staff should also be trained to recognize social engineering: a convincing caller requesting a guest’s room number, a fake supplier invoice, or a fraudulent reset request can bypass technical safeguards surprisingly quickly.
4. Build emergency procedures around people under pressure
In a real emergency, employees do not consult a lengthy policy manual page by page. They act on what they remember, what equipment is available, and whether the escalation chain is clear. That is why drills, concise role cards, accessible communications, and post-event learning are essential compliance evidence—not optional extras.
Emergency planning should reflect the property’s location and operating model. An urban business hotel may prioritize medical events, suspicious packages, protest activity, and high-volume evacuation. A coastal resort may need detailed storm, flood, heat, water safety, and temporary shelter procedures. Remote eco-lodges and glamping sites require special attention to communications resilience, evacuation routes, fire spread, wildlife hazards, and delayed emergency-service response.
- Maintain tested plans for fire, medical emergencies, violence or threatening behavior, missing persons, severe weather, utility failure, and cyber-related operational disruption.
- Provide reliable emergency contact lists and escalation thresholds for duty managers.
- Ensure procedures address guests with disabilities, children, non-native speakers, and guests who may need medical assistance.
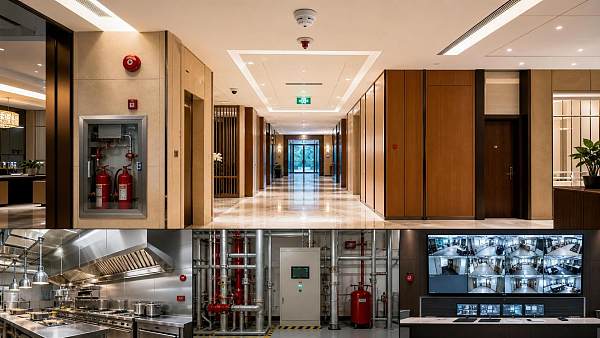
- Inspect emergency lighting, alarms, extinguishers, first-aid supplies, evacuation signage, and assembly-point instructions on a defined schedule.
- Run exercises that include night operations, reduced staffing, and realistic communication constraints.
- Record drill results, gaps identified, owners of corrective actions, and completion dates.
A response plan should also protect staff from being left alone with an escalating situation. Lone-worker measures, duress alarms, radio protocols, buddy systems, and manager call-out arrangements deserve particular attention in housekeeping, night audit, parking operations, maintenance, and remote site management.
5. Make staff training observable and role-specific
Security awareness training is often recorded as a completed module, then forgotten. A stronger approach checks whether a receptionist knows how to handle a request for a guest’s whereabouts; whether housekeeping can identify a compromised door lock; whether a night manager can preserve evidence; and whether maintenance personnel understand the approval process for vendor access.
Training should be concise enough to retain, repeated often enough to remain useful, and tailored to actual job roles. It should include de-escalation, privacy, suspicious activity reporting, safe handling of lost property, child safeguarding where relevant, incident documentation, and the limits of staff authority.
Quality managers should sample training records and then validate competence in the field through spot questions, tabletop scenarios, and observed drills. Completion rates alone do not show whether the protocol will work at 2 a.m. during a power interruption.
6. Extend the checklist to vendors, furnishings, and built assets
Security risks are frequently introduced through procurement decisions. A contractor may receive broad access without screening or supervision. A smart lock may be purchased without considering credential lifecycle management. A decorative partition, modular cabin component, or hospitality furnishing may obstruct sightlines, impede egress, create a fire-safety issue, or fail under heavy public use.
Supplier review should therefore assess more than price, appearance, and delivery dates. Request technical documentation, maintenance requirements, applicable test evidence, software support commitments, material specifications, privacy responsibilities, and warranty limitations. For prefabricated and eco-structures, examine structural resilience, fire performance, weather resistance, utility interfaces, secure openings, and emergency access from the earliest design stage.
TerraVista Metrics supports this evidence-based approach by connecting hospitality decision-makers with technical benchmarking, regulatory analysis, and supply-chain intelligence. For a security manager, the value lies in asking better procurement questions before systems are installed and before vulnerabilities become expensive to correct.
A practical audit rhythm: monthly checks, annual reassessment
Not every control needs the same review frequency. Daily checks may cover key custody, alarm status, staffing, and incident logs. Monthly reviews can test access permissions, camera functionality, emergency supplies, contractor records, and open corrective actions. At least annually—and after a major renovation, system change, serious incident, or change in local risk—conduct a broader risk assessment.
Keep the audit trail practical: finding, risk level, required action, responsible person, due date, verification method, and closure evidence. This turns a checklist into a management tool rather than a document prepared only for inspection day.
The most resilient hotels do not promise that incidents will never occur. They create conditions in which risks are recognized early, staff know what to do, systems support rather than confuse the response, and lessons lead to measurable improvement. That is the real purpose of compliant security protocols for hospitality: protecting the people who trust a property with their safety, their privacy, and their time away from home.
Recommended News
 Oct 04, 2026A Procurement Checklist for Tourism Hardware Equipment in Resorts and Visitor CentersTourism hardware equipment procurement checklist for resorts and visitor centers: compare durability, compliance, lifecycle costs, supplier support, and logistics.
 Sep 23, 2026Planning Smart Classroom Solutions for Hybrid Learning Without Creating AV Support GapsSmart classroom solutions for reliable hybrid learning: standardize workflows, strengthen AV support, and deliver seamless teaching experiences.
 Sep 11, 2026Hotel Security Protocols: A Compliance Checklist for Protecting Guests and StaffSecurity protocols for hospitality: use this practical hotel compliance checklist to protect guests, staff, data, access points, and emergency operations.
 Sep 03, 2026How to Plan Theme Park Infrastructure for Mixed-Use DevelopmentsTheme park infrastructure for mixed use developments: plan resilient utilities, circulation, attractions, hospitality, and digital systems for scalable destinations.
 Aug 23, 2026What Makes Community Based Eco Resort Development Successful in Rural Destinations?Community based eco resort development succeeds when land fit, local participation, infrastructure, and operations align. Discover practical strategies for resilient, high-value rural eco resorts.
 Aug 21, 2026How Many Rooms Should an Eco Resort Have to Balance ROI and Guest Experience?Eco resort development room count directly shapes ROI, infrastructure efficiency, and guest privacy. Learn how to choose the right key range to protect margins and elevate the experience.
 Aug 15, 2026How to Analyze Stainless Steel Fatigue in Cyclic Load ApplicationsStainless steel fatigue analysis helps you spot hidden cyclic load risks early, improve reliability, and prevent costly failures in real-world applications.
 Aug 08, 2026Hospitality Engineering Standards for Resorts: Key Compliance Checks Before Design ApprovalHospitality engineering standards for resorts explained: discover the key compliance checks before design approval to avoid delays, reduce risk, and build guest-ready, resilient resort projects.
 Jul 21, 2026Tourism Destination Infrastructure Solutions: How to Plan Smarter Visitor FacilitiesTourism destination infrastructure solutions for smarter visitor facilities: learn how to reduce risk, improve uptime, and plan scalable, data-backed destinations that perform long term.
 Jul 19, 2026How to Choose Rustproof Hotel Furniture for Coastal and High-Humidity PropertiesRustproof hotel furniture is essential for coastal and high-humidity properties. Learn how to compare materials, finishes, and supplier claims to reduce maintenance costs and extend service life.
 Jul 16, 2026How to Choose Resort Bar Furniture for Outdoor Hospitality SpacesResort bar furniture buying guide for outdoor hospitality spaces: compare materials, durability, comfort, and maintenance to choose stylish, long-lasting commercial pieces.
 Jul 15, 2026Commercial Thermal Efficiency Testing: Key Metrics, Test Methods, and Compliance BasicsCommercial thermal efficiency testing explained: learn key metrics, test methods, common compliance risks, and practical steps to improve performance, cut costs, and make smarter asset decisions.
 Jul 14, 2026Smart Tourism Integration vs Standalone Systems: Which Setup Fits Multi-Site Operations?Smart tourism integration or standalone systems? Discover which setup best fits multi-site tourism operations, improves visibility, compliance, scalability, and guest experience.
 Jul 13, 2026Export Market Opportunities in Latin America: How to Identify Profitable Entry PointsExport market opportunities in Latin America are shifting toward high-margin, compliant sectors. Discover how to spot profitable entry points in tourism, hospitality, and smart infrastructure.
 Jul 12, 2026Carbon Compliance in North America: Key Reporting Rules and Risk Points for ManufacturersCarbon compliance North America: learn the key U.S. and Canada reporting rules, top risk points for manufacturers, and how to strengthen data, supplier checks, and compliance readiness.
 Jul 11, 2026How to Evaluate Coated Surface Structural Performance Testing for Outdoor InstallationsCoated surface structural performance testing for outdoor installations: learn how to assess adhesion, crack resistance, corrosion durability, and real-world structural risk before procurement.
 Jul 10, 2026Outdoor Furniture Durability Cost: Which Materials Last Longer and Cost Less to Maintain?Outdoor furniture durability cost explained: compare aluminum, teak, steel, and HDPE to find materials that last longer, reduce maintenance, and deliver better long-term value.
 Jul 09, 2026Technical Integration Security: Key Standards, System Architecture, and Risk ChecksTechnical integration security explained: explore key standards, system architecture signals, and risk checks to build resilient, compliant, and scalable connected infrastructure.
 Jul 08, 2026Tourism Asset Evaluation in Middle East: Key Metrics for Hotel and Resort ProjectsTourism asset evaluation in Middle East explained through key metrics for hotel and resort projects, covering location, infrastructure, lifecycle cost, sustainability, and technology.
![]() Jul 07, 2026Eco Building Materials Manufacturer Checklist: Certifications, MOQ, and Custom OptionsEco building materials manufacturer checklist covering certifications, MOQ, and custom options. Learn how to compare suppliers, reduce project risk, and choose sustainable materials with confidence.
 Jul 06, 2026Hospitality Fire Safety Standards Explained: Key Compliance Points for Hotels and ResortsHospitality fire safety standards explained for hotels and resorts: learn key compliance points, risk areas, and practical steps to protect guests, assets, and operations.
 Jul 03, 2026How to Specify High Traffic Furniture Weight Capacity for Hotels, Lobbies, and Public AreasHigh traffic furniture weight capacity for hotels, lobbies, and public areas: learn how to verify load ratings, testing standards, and durability specs to reduce risk and choose smarter.
 Jul 03, 2026Hospitality Procurement Finish Standards Explained: How to Compare Durability, Cost, and ComplianceHospitality procurement finish standards explained: compare durability, lifecycle cost, and compliance with a practical framework for smarter sourcing and fewer costly project delays.
 Jun 30, 2026Tourism Equipment Evaluation Compliance: What to Check Before Purchase and Site DeploymentTourism equipment evaluation compliance: learn what to verify before purchase and site deployment to reduce risk, control costs, ensure safety, and choose suppliers with confidence.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.