Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- Hotel Security Protocols: A Compliance Checklist for Protecting Guests and StaffSecurity protocols for hospitality: use this practical hotel compliance checklist to protect guests, staff, data, access points, and emergency operations.
- How to Evaluate Resort Slide System Suppliers for Safety, Capacity, and Project SupportResort slide systems supplier evaluation guide: compare safety evidence, real capacity, durable materials, and project support for confident resort investments.
- Sustainable Building Materials Pricing: How Buyers Compare Cost, Life Cycle, and RiskSustainable building materials pricing explained: compare installed cost, life-cycle value, carbon evidence, and supply-chain risk for smarter procurement decisions.
Popular Tags
TerraVista Metrics (TVM)Industry NewsTechnical Integration Security: Key Standards, System Architecture, and Risk Checks
auth.Time
Sep 09, 2026Click Count
Technical Integration Security: Key Standards, System Architecture, and Risk Checks
For technical evaluators, technical integration security is no longer a secondary checkpoint but a core requirement for resilient tourism infrastructure.
From smart hotel ecosystems to prefabricated guest assets, every connected system needs clear standards, stable architecture, and repeatable risk checks.
That shift is especially visible in tourism projects where hardware, software, energy systems, guest services, and supplier networks must operate as one environment.
In practice, technical integration security determines whether a deployment is merely connected or truly dependable under commercial pressure.
This matters across modular resorts, smart hotels, attraction systems, leisure assets, and hospitality furnishing with embedded controls.
A useful review should therefore combine standards mapping, architecture inspection, supplier validation, and operational risk testing in one consistent method.
Why Technical Integration Security Has Become a Board-Level Issue
Tourism infrastructure now relies on layered systems rather than isolated assets.
A guest cabin may include HVAC controls, access management, occupancy sensing, payment interfaces, and cloud reporting.
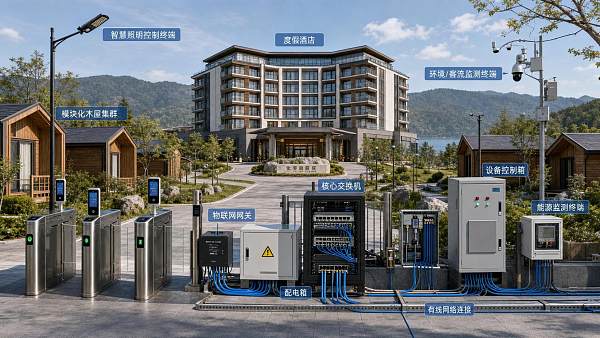
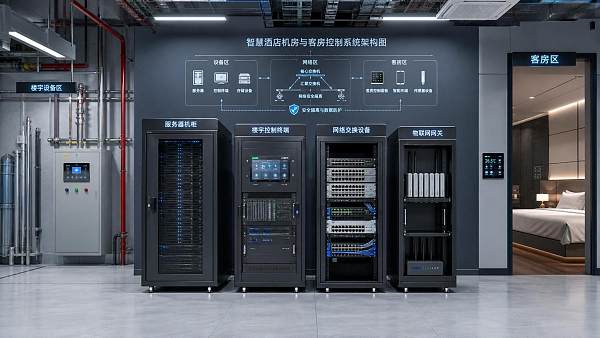
A hotel network may link room automation, PMS, BMS, IoT gateways, surveillance, and AI operations tools.
Once these elements share data and commands, the security question is no longer only cyber.
It becomes an integration problem involving protocol trust, failover behavior, device identity, configuration drift, and vendor dependency.
More importantly, weak technical integration security often shows up as downtime, safety events, compliance gaps, or procurement waste.
That is why engineering reviews now need to test not only what each component can do, but how the full system behaves together.
Core Standards That Shape Technical Integration Security
A strong evaluation starts with standards, but not every standard has the same role.
Some define security governance. Others define interoperability, data handling, or industrial control resilience.
The most relevant references usually include:
- ISO/IEC 27001 for information security management structure.
- ISO/IEC 62443 for industrial and operational technology security.
- NIST Cybersecurity Framework for risk-based control mapping.
- ISO 22301 where business continuity affects integrated guest operations.
- GDPR and local privacy rules for guest and workforce data flows.
- BACnet, KNX, Modbus, OPC UA, MQTT, and similar protocol standards for device communication.
The practical point is simple.
Technical integration security should be assessed at the intersection of these frameworks, not through a single certificate.
A vendor may be compliant on paper, yet still expose a weak integration path between field devices and cloud services.
System Architecture Signals That Deserve Immediate Attention
Architecture review is where technical integration security becomes visible.
Instead of asking whether a device is secure, ask how trust is maintained across the full stack.
Several architecture signals deserve close attention:
- Network segmentation between guest, operational, safety, and supplier domains.
- Secure gateway design for translating between legacy protocols and cloud platforms.
- Centralized identity and access control for users, services, and devices.
- Logging architecture that supports traceability across edge and cloud layers.
- Fail-safe and fail-secure behavior when links, power, or external services drop.
- Update paths for firmware, middleware, API clients, and orchestration tools.
This is where many deployments become fragile.
Legacy building controls may be stable alone, but unsafe once exposed through remote dashboards or mobile guest applications.
A sound technical integration security review should show exactly where data enters, where commands propagate, and where failure can spread.
How to Evaluate Interoperability Without Missing Security Gaps
Interoperability is often treated as a functional checkbox.
In reality, it is one of the biggest technical integration security variables in tourism infrastructure.
Every protocol bridge, API adapter, or custom middleware layer adds attack surface and maintenance complexity.
A useful interoperability review should verify:
- Whether interfaces use open standards or vendor-specific connectors.
- Whether encryption and authentication survive protocol translation.
- Whether timestamps, alarms, and event priorities stay consistent across systems.
- Whether disconnected mode is defined for edge locations with unstable connectivity.
- Whether data ownership and export rights remain clear after integration.
This also affects commercial resilience.
If a site cannot replace one subsystem without rebuilding the whole stack, technical integration security is already compromised by lock-in.
That is why open, documented, testable interfaces remain a serious procurement criterion, not just an engineering preference.
Risk Checks That Should Be Standard Before Approval
A mature technical integration security process depends on evidence, not vendor claims.
Before approval, the following checks should be routine:
These checks are not excessive.
They are the minimum needed to prove that technical integration security will hold under real operating conditions.
In remote resorts, seasonal attractions, and distributed hospitality sites, weak recovery design can be as damaging as an outright breach.
What Strong Evaluation Looks Like in Tourism Infrastructure
The tourism sector adds a few conditions that standard enterprise reviews often miss.
Sites are often geographically dispersed, supplier-built, weather-exposed, and dependent on mixed legacy and modern assets.
That means technical integration security should be judged against field reality, not only lab assumptions.
For example, a strong review should answer questions like these:
- Can a modular guest unit operate safely during network loss?
- Can hotel IoT traffic be isolated from guest Wi-Fi and entertainment devices?
- Can attraction control systems remain stable during supplier maintenance sessions?
- Can furnishing or room controls be replaced without rewriting the management platform?
- Can procurement teams compare vendors using equivalent security and interoperability evidence?
This is exactly where data-driven benchmarking becomes valuable.
Organizations such as TerraVista Metrics help translate technical integration security into measurable acceptance criteria, comparable supplier evidence, and lower deployment risk.
A Practical Decision Framework for the Next Review Cycle
The next review cycle should start with a simple principle.
Technical integration security is not a final-stage audit item.
It belongs at concept design, vendor selection, factory acceptance, site commissioning, and post-launch change control.
A practical framework usually follows five steps:
- Define the critical services that cannot fail.
- Map standards and compliance duties to each integration layer.
- Inspect architecture for segmentation, identity, logging, and fallback behavior.
- Run evidence-based risk checks before commercial sign-off.
- Maintain a change register for suppliers, firmware, APIs, and remote access rights.
That sequence keeps technical integration security tied to operational reality.
It also helps procurement, engineering, and site operations work from the same evidence base.
As tourism infrastructure becomes more connected, that shared discipline will separate scalable projects from expensive, fragile ones.
The immediate next move is clear: review every new deployment through the lens of technical integration security before interoperability problems become operational risk.
Recommended News
 Sep 11, 2026Hotel Security Protocols: A Compliance Checklist for Protecting Guests and StaffSecurity protocols for hospitality: use this practical hotel compliance checklist to protect guests, staff, data, access points, and emergency operations.
 Sep 03, 2026How to Plan Theme Park Infrastructure for Mixed-Use DevelopmentsTheme park infrastructure for mixed use developments: plan resilient utilities, circulation, attractions, hospitality, and digital systems for scalable destinations.
 Aug 23, 2026What Makes Community Based Eco Resort Development Successful in Rural Destinations?Community based eco resort development succeeds when land fit, local participation, infrastructure, and operations align. Discover practical strategies for resilient, high-value rural eco resorts.
 Aug 21, 2026How Many Rooms Should an Eco Resort Have to Balance ROI and Guest Experience?Eco resort development room count directly shapes ROI, infrastructure efficiency, and guest privacy. Learn how to choose the right key range to protect margins and elevate the experience.
 Aug 15, 2026How to Analyze Stainless Steel Fatigue in Cyclic Load ApplicationsStainless steel fatigue analysis helps you spot hidden cyclic load risks early, improve reliability, and prevent costly failures in real-world applications.
 Aug 08, 2026Hospitality Engineering Standards for Resorts: Key Compliance Checks Before Design ApprovalHospitality engineering standards for resorts explained: discover the key compliance checks before design approval to avoid delays, reduce risk, and build guest-ready, resilient resort projects.
 Jul 21, 2026Tourism Destination Infrastructure Solutions: How to Plan Smarter Visitor FacilitiesTourism destination infrastructure solutions for smarter visitor facilities: learn how to reduce risk, improve uptime, and plan scalable, data-backed destinations that perform long term.
 Jul 19, 2026How to Choose Rustproof Hotel Furniture for Coastal and High-Humidity PropertiesRustproof hotel furniture is essential for coastal and high-humidity properties. Learn how to compare materials, finishes, and supplier claims to reduce maintenance costs and extend service life.
 Jul 16, 2026How to Choose Resort Bar Furniture for Outdoor Hospitality SpacesResort bar furniture buying guide for outdoor hospitality spaces: compare materials, durability, comfort, and maintenance to choose stylish, long-lasting commercial pieces.
 Jul 15, 2026Commercial Thermal Efficiency Testing: Key Metrics, Test Methods, and Compliance BasicsCommercial thermal efficiency testing explained: learn key metrics, test methods, common compliance risks, and practical steps to improve performance, cut costs, and make smarter asset decisions.
 Jul 14, 2026Smart Tourism Integration vs Standalone Systems: Which Setup Fits Multi-Site Operations?Smart tourism integration or standalone systems? Discover which setup best fits multi-site tourism operations, improves visibility, compliance, scalability, and guest experience.
 Jul 13, 2026Export Market Opportunities in Latin America: How to Identify Profitable Entry PointsExport market opportunities in Latin America are shifting toward high-margin, compliant sectors. Discover how to spot profitable entry points in tourism, hospitality, and smart infrastructure.
 Jul 12, 2026Carbon Compliance in North America: Key Reporting Rules and Risk Points for ManufacturersCarbon compliance North America: learn the key U.S. and Canada reporting rules, top risk points for manufacturers, and how to strengthen data, supplier checks, and compliance readiness.
 Jul 11, 2026How to Evaluate Coated Surface Structural Performance Testing for Outdoor InstallationsCoated surface structural performance testing for outdoor installations: learn how to assess adhesion, crack resistance, corrosion durability, and real-world structural risk before procurement.
 Jul 10, 2026Outdoor Furniture Durability Cost: Which Materials Last Longer and Cost Less to Maintain?Outdoor furniture durability cost explained: compare aluminum, teak, steel, and HDPE to find materials that last longer, reduce maintenance, and deliver better long-term value.
 Jul 09, 2026Technical Integration Security: Key Standards, System Architecture, and Risk ChecksTechnical integration security explained: explore key standards, system architecture signals, and risk checks to build resilient, compliant, and scalable connected infrastructure.
 Jul 08, 2026Tourism Asset Evaluation in Middle East: Key Metrics for Hotel and Resort ProjectsTourism asset evaluation in Middle East explained through key metrics for hotel and resort projects, covering location, infrastructure, lifecycle cost, sustainability, and technology.
![]() Jul 07, 2026Eco Building Materials Manufacturer Checklist: Certifications, MOQ, and Custom OptionsEco building materials manufacturer checklist covering certifications, MOQ, and custom options. Learn how to compare suppliers, reduce project risk, and choose sustainable materials with confidence.
 Jul 06, 2026Hospitality Fire Safety Standards Explained: Key Compliance Points for Hotels and ResortsHospitality fire safety standards explained for hotels and resorts: learn key compliance points, risk areas, and practical steps to protect guests, assets, and operations.
 Jul 03, 2026How to Specify High Traffic Furniture Weight Capacity for Hotels, Lobbies, and Public AreasHigh traffic furniture weight capacity for hotels, lobbies, and public areas: learn how to verify load ratings, testing standards, and durability specs to reduce risk and choose smarter.
 Jul 03, 2026Hospitality Procurement Finish Standards Explained: How to Compare Durability, Cost, and ComplianceHospitality procurement finish standards explained: compare durability, lifecycle cost, and compliance with a practical framework for smarter sourcing and fewer costly project delays.
 Jun 30, 2026Tourism Equipment Evaluation Compliance: What to Check Before Purchase and Site DeploymentTourism equipment evaluation compliance: learn what to verify before purchase and site deployment to reduce risk, control costs, ensure safety, and choose suppliers with confidence.
 Jun 28, 2026How to Select Durable Hotel Furniture for Waiting Areas with High Guest TurnoverDurable hotel furniture for waiting areas: learn how to choose seating and surfaces that withstand high guest turnover, reduce maintenance costs, and protect your hotel’s first impression.
 Jun 27, 2026Sustainable Tourism Construction: 7 Design Priorities for Low-Impact Hospitality ProjectsSustainable tourism construction: discover 7 design priorities for low-impact hospitality projects that cut risk, improve lifecycle performance, and boost guest, investor, and ESG value.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.