Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- How to Evaluate Spark Plug Suppliers for Consistent Quality and Lead TimesSpark plugs supplier evaluation guide: compare quality control, traceability, fitment, total cost, and reliable lead times to secure dependable engine maintenance supply.
- What Drives System Interoperability Testing Service Costs in Complex Projects?System interoperability testing service cost depends on integration scope, workflows, environments, and assurance needs. Learn how to budget smarter and reduce project risk.
- Project Planning Sourcing Guides: How to Qualify Suppliers Before Work StartsSourcing guides project planning helps teams qualify suppliers before work begins—verify compliance, delivery capacity, financial strength, and sustainability to reduce risk and protect project outcomes.
Popular Tags
TerraVista Metrics (TVM)Industry NewsTechnical Procurement and CE Compliance: What Buyers Need to Check Before Ordering
auth.Time
Oct 07, 2026Click Count
Why does technical procurement CE compliance matter before an order is placed?
In technical procurement, CE compliance is not a formality added after commercial approval. It is part of the buying decision itself.
A missing declaration, weak test basis, or incorrect label can stop a shipment, delay installation, or expose an operator to avoidable safety risk.
That becomes especially relevant in tourism projects, where equipment often combines public use, outdoor exposure, electrical integration, and cross-border sourcing.
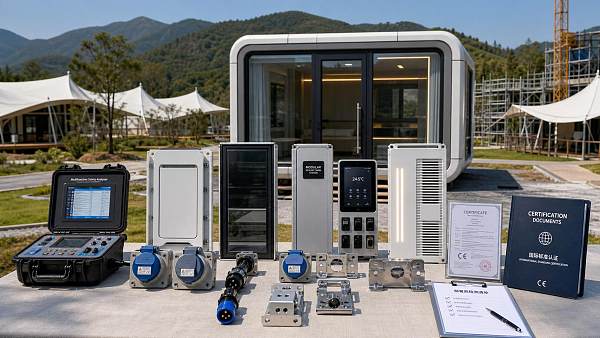
A modular cabin controller, smart hotel gateway, attraction component, or commercial furnishing accessory may all raise different compliance questions.
The practical goal is simple. Buyers need evidence that the product is safe, correctly assessed, and legally placeable on the intended market.
This is where technical procurement CE compliance becomes a risk-control process, not just a document collection exercise.
Across tourism infrastructure, TerraVista Metrics often frames procurement around measurable performance, traceable documentation, and fit-for-use verification.
That perspective matters because attractive product claims do not always match engineering reality, especially in fast-moving international supply chains.
What should be checked first: the CE mark, or the evidence behind it?
The CE mark should never be the starting point by itself. The better question is whether the mark is supported by the correct technical file.
In practice, the first review usually covers four items: product identity, applicable directives, test evidence, and the Declaration of Conformity.
If one of those items is inconsistent, the mark may be present while the compliance basis remains weak.
- Check whether the model number on reports matches the ordered version exactly.
- Confirm that relevant directives are named, not implied.
- Review whether standards cited are current and appropriate for the product function.
- Make sure the Declaration of Conformity identifies the legal manufacturer.
A common mistake is accepting a laboratory report without checking scope. Some reports cover components, not the final assembled product.
Another issue appears when one report is reused across several variants with different power ratings, enclosures, or safety functions.
For technical procurement CE compliance, that difference matters because even small design changes can alter the required assessment path.
A quick document check helps separate valid files from decorative paperwork
Used this way, the table becomes more than an admin checklist. It helps determine whether the supplier understands compliance at system level.
Which products usually need deeper review, even when the paperwork looks complete?
The higher the interaction between safety, electronics, structure, and public use, the deeper the review should be.
That is often true in mixed-use tourism assets. Smart access systems, EV-linked cabins, networked room controls, ride subsystems, and outdoor powered gear deserve closer attention.
Why? Because technical procurement CE compliance can become blurred when the ordered item sits between component and final system.
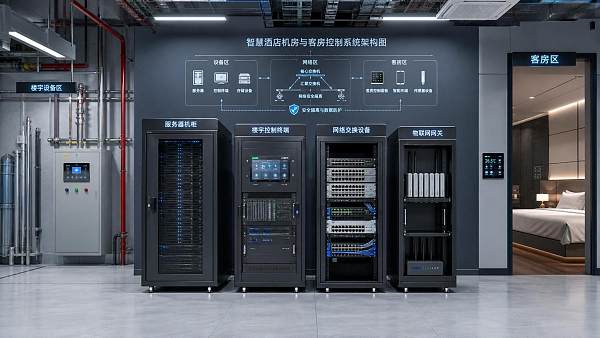
For example, a hotel IoT gateway may comply as equipment, yet still create project risk if cybersecurity, interoperability, and installation conditions are undefined.
A prefabricated unit may include compliant subassemblies, while the integrated installation raises new questions on low voltage, EMC, or machinery interfaces.
More specialized attraction equipment can introduce fatigue, guarding, emergency stop logic, and maintenance access issues that standard brochures rarely explain.
This is one reason benchmark-focused organizations such as TerraVista Metrics emphasize verified performance reports alongside regulatory review.
The documents may be compliant on paper, yet still fail to answer whether the asset is durable, interoperable, and suitable for heavy public operation.
How can buyers judge whether test reports and supplier claims are actually reliable?
Reliability is usually judged through consistency, not through a single certificate.
Start by comparing the quotation, product datasheet, report, declaration, label artwork, and installation manual. The story should stay the same across all files.
If rated voltage changes between documents, or if dimensions differ, that is not a minor clerical issue. It may indicate uncontrolled revision status.
A stronger review also looks at the laboratory source, report issue date, sample description, and any noted limitations.
- Ask whether the tested sample reflects normal production.
- Check whether critical materials or suppliers changed after testing.
- Confirm who controls firmware, safety settings, and version history.
- Review whether warnings and limitations are passed into site documentation.
In real projects, supplier traceability often becomes the deciding factor. If there is no clear revision trail, compliance confidence remains weak.
Technical procurement CE compliance should therefore include batch records, component sourcing logic, and change notification expectations before the purchase order is released.
What are the most common CE compliance mistakes before ordering?
The most frequent mistakes are surprisingly ordinary. They happen when commercial speed outruns technical review.
One mistake is treating CE compliance as the supplier’s issue only. In reality, ordering the wrong product version creates downstream responsibility for the buyer and operator.
Another is assuming that previous imports prove present compliance. Standards, directives, and product configurations change over time.
There is also confusion between test completion and market readiness. A test report supports compliance, but it does not replace full technical procurement CE compliance review.
More subtle problems tend to appear in these areas:
- Instructions lack safe installation limits for site conditions.
- The importer or legal manufacturer is not clearly identified.
- Labeling omits serial traceability or electrical ratings.
- Declarations cite standards irrelevant to the product category.
- Supplier updates materials without re-evaluating risk.
In public-facing sectors such as hospitality, outdoor leisure, and attractions, these gaps can become operational problems very quickly.
A delayed opening, failed inspection, or replacement cycle often costs far more than an early technical review.
How do cost, lead time, and risk change when compliance is checked early?
Early review rarely makes procurement slower in any meaningful way. More often, it prevents expensive stop-and-correct work later.
When technical procurement CE compliance is reviewed before ordering, three benefits usually follow.
- Specification errors are caught before manufacturing starts.
- Documentation gaps are corrected before customs or site inspection.
- Alternative suppliers can still be compared without sunk-cost pressure.
This matters even more for tourism development, where opening schedules, guest safety, and brand reputation are tightly linked.
A benchmark-driven review can also improve capital allocation. Instead of buying on appearance or broad claims, teams compare tested performance against real operating demands.
That approach aligns with the broader role TerraVista Metrics plays across eco-structures, smart hotel systems, outdoor gear, attractions, and hospitality furnishing.
The point is not to add bureaucracy. The point is to make each order technically defensible, commercially practical, and safer to deploy.
What should the final pre-order checklist include?
Before release, the review should end with a short decision file, not a scattered email trail.
A workable checklist usually includes the product version, intended use, applicable directives, supporting reports, declaration status, label sample, manual review, and traceability route.
It should also record unresolved assumptions. If a product is compliant only under certain installation conditions, that needs to be visible before shipment.
For higher-risk categories, add a trigger for re-review when firmware, materials, enclosure design, or key suppliers change.
That final step turns technical procurement CE compliance into a repeatable internal standard rather than a one-off reaction.
A sensible next move is to map upcoming orders by risk level, then compare documentation depth against actual application conditions.
Where gaps appear, use verified test data, compliance review, and supplier traceability checks to close them before the order is placed.
Recommended News
 Oct 04, 2026A Procurement Checklist for Tourism Hardware Equipment in Resorts and Visitor CentersTourism hardware equipment procurement checklist for resorts and visitor centers: compare durability, compliance, lifecycle costs, supplier support, and logistics.
 Sep 23, 2026Planning Smart Classroom Solutions for Hybrid Learning Without Creating AV Support GapsSmart classroom solutions for reliable hybrid learning: standardize workflows, strengthen AV support, and deliver seamless teaching experiences.
 Sep 11, 2026Hotel Security Protocols: A Compliance Checklist for Protecting Guests and StaffSecurity protocols for hospitality: use this practical hotel compliance checklist to protect guests, staff, data, access points, and emergency operations.
 Sep 03, 2026How to Plan Theme Park Infrastructure for Mixed-Use DevelopmentsTheme park infrastructure for mixed use developments: plan resilient utilities, circulation, attractions, hospitality, and digital systems for scalable destinations.
 Aug 23, 2026What Makes Community Based Eco Resort Development Successful in Rural Destinations?Community based eco resort development succeeds when land fit, local participation, infrastructure, and operations align. Discover practical strategies for resilient, high-value rural eco resorts.
 Aug 21, 2026How Many Rooms Should an Eco Resort Have to Balance ROI and Guest Experience?Eco resort development room count directly shapes ROI, infrastructure efficiency, and guest privacy. Learn how to choose the right key range to protect margins and elevate the experience.
 Aug 15, 2026How to Analyze Stainless Steel Fatigue in Cyclic Load ApplicationsStainless steel fatigue analysis helps you spot hidden cyclic load risks early, improve reliability, and prevent costly failures in real-world applications.
 Aug 08, 2026Hospitality Engineering Standards for Resorts: Key Compliance Checks Before Design ApprovalHospitality engineering standards for resorts explained: discover the key compliance checks before design approval to avoid delays, reduce risk, and build guest-ready, resilient resort projects.
 Jul 21, 2026Tourism Destination Infrastructure Solutions: How to Plan Smarter Visitor FacilitiesTourism destination infrastructure solutions for smarter visitor facilities: learn how to reduce risk, improve uptime, and plan scalable, data-backed destinations that perform long term.
 Jul 19, 2026How to Choose Rustproof Hotel Furniture for Coastal and High-Humidity PropertiesRustproof hotel furniture is essential for coastal and high-humidity properties. Learn how to compare materials, finishes, and supplier claims to reduce maintenance costs and extend service life.
 Jul 16, 2026How to Choose Resort Bar Furniture for Outdoor Hospitality SpacesResort bar furniture buying guide for outdoor hospitality spaces: compare materials, durability, comfort, and maintenance to choose stylish, long-lasting commercial pieces.
 Jul 15, 2026Commercial Thermal Efficiency Testing: Key Metrics, Test Methods, and Compliance BasicsCommercial thermal efficiency testing explained: learn key metrics, test methods, common compliance risks, and practical steps to improve performance, cut costs, and make smarter asset decisions.
 Jul 14, 2026Smart Tourism Integration vs Standalone Systems: Which Setup Fits Multi-Site Operations?Smart tourism integration or standalone systems? Discover which setup best fits multi-site tourism operations, improves visibility, compliance, scalability, and guest experience.
 Jul 13, 2026Export Market Opportunities in Latin America: How to Identify Profitable Entry PointsExport market opportunities in Latin America are shifting toward high-margin, compliant sectors. Discover how to spot profitable entry points in tourism, hospitality, and smart infrastructure.
 Jul 12, 2026Carbon Compliance in North America: Key Reporting Rules and Risk Points for ManufacturersCarbon compliance North America: learn the key U.S. and Canada reporting rules, top risk points for manufacturers, and how to strengthen data, supplier checks, and compliance readiness.
 Jul 11, 2026How to Evaluate Coated Surface Structural Performance Testing for Outdoor InstallationsCoated surface structural performance testing for outdoor installations: learn how to assess adhesion, crack resistance, corrosion durability, and real-world structural risk before procurement.
 Jul 10, 2026Outdoor Furniture Durability Cost: Which Materials Last Longer and Cost Less to Maintain?Outdoor furniture durability cost explained: compare aluminum, teak, steel, and HDPE to find materials that last longer, reduce maintenance, and deliver better long-term value.
 Jul 09, 2026Technical Integration Security: Key Standards, System Architecture, and Risk ChecksTechnical integration security explained: explore key standards, system architecture signals, and risk checks to build resilient, compliant, and scalable connected infrastructure.
 Jul 08, 2026Tourism Asset Evaluation in Middle East: Key Metrics for Hotel and Resort ProjectsTourism asset evaluation in Middle East explained through key metrics for hotel and resort projects, covering location, infrastructure, lifecycle cost, sustainability, and technology.
![]() Jul 07, 2026Eco Building Materials Manufacturer Checklist: Certifications, MOQ, and Custom OptionsEco building materials manufacturer checklist covering certifications, MOQ, and custom options. Learn how to compare suppliers, reduce project risk, and choose sustainable materials with confidence.
 Jul 06, 2026Hospitality Fire Safety Standards Explained: Key Compliance Points for Hotels and ResortsHospitality fire safety standards explained for hotels and resorts: learn key compliance points, risk areas, and practical steps to protect guests, assets, and operations.
 Jul 03, 2026How to Specify High Traffic Furniture Weight Capacity for Hotels, Lobbies, and Public AreasHigh traffic furniture weight capacity for hotels, lobbies, and public areas: learn how to verify load ratings, testing standards, and durability specs to reduce risk and choose smarter.
 Jul 03, 2026Hospitality Procurement Finish Standards Explained: How to Compare Durability, Cost, and ComplianceHospitality procurement finish standards explained: compare durability, lifecycle cost, and compliance with a practical framework for smarter sourcing and fewer costly project delays.
 Jun 30, 2026Tourism Equipment Evaluation Compliance: What to Check Before Purchase and Site DeploymentTourism equipment evaluation compliance: learn what to verify before purchase and site deployment to reduce risk, control costs, ensure safety, and choose suppliers with confidence.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.