Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- How to Plan Outdoor Kinetic Art Installations for Parks, Resorts, and Public SpacesOutdoor kinetic art planning guide for parks, resorts, and public spaces—explore safety, engineering, materials, lifecycle costs, and maintenance for lasting visitor impact.
- Amusement Equipment Testing for Family Entertainment Centers: Key Safety ChecksAmusement equipment testing for family entertainment centers: discover essential safety checks for restraints, brakes, interlocks, structural wear, and daily operations.
- What Engineering Performance Testing Should Cover During a Specification ReviewEngineering performance testing for specification review: learn how to verify structural strength, durability, safety, sustainability, and system reliability before costly project decisions.
Popular Tags
TerraVista Metrics (TVM)Industry NewsRegulatory Compliance Framework Explained: Core Elements, Gaps, and Audit Readiness
auth.Time
Sep 05, 2026Click Count
A strong regulatory compliance framework has become a working requirement for organizations operating across complex supply chains, technical standards, and public-facing assets. In tourism-linked development, the issue is even sharper. Projects now combine built structures, connected systems, safety equipment, sustainability claims, and cross-border sourcing. That mix creates exposure far beyond a single legal checklist. A practical framework helps translate regulation into operating discipline, reduces audit friction, and gives leadership a clearer basis for investment decisions.
What a regulatory compliance framework really covers
At its core, a regulatory compliance framework is the structure used to identify obligations, assign ownership, document controls, monitor evidence, and respond when gaps appear.
That sounds simple, but the scope is often broader than expected.
For one organization, it may include building codes, product safety rules, environmental reporting, data protection, cybersecurity, labor requirements, import documentation, and sector-specific certifications.
In practice, the framework is not just a policy file. It is the link between regulatory intent and everyday decisions, from procurement approvals to maintenance logs and vendor onboarding.
A useful way to view it is as an operating map. It shows what must be complied with, where the evidence sits, who owns the action, and how quickly the organization can prove control.
Why the topic matters more now
Regulatory pressure is rising because business models have become more integrated. Physical infrastructure is tied to digital systems, sustainability claims are scrutinized, and supply chains stretch across multiple jurisdictions.
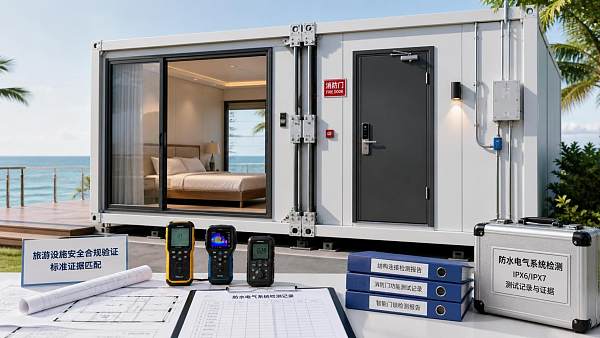
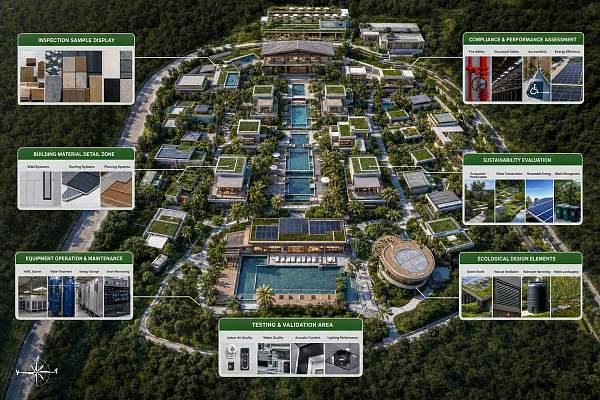
A hospitality site may depend on modular units, IoT networks, imported furnishings, visitor safety hardware, and energy performance targets at the same time.
Each layer brings a different set of obligations.
This is where a mature regulatory compliance framework becomes commercially relevant. It supports more accurate budgeting, reduces rework, protects timelines, and limits the cost of late-stage corrections.
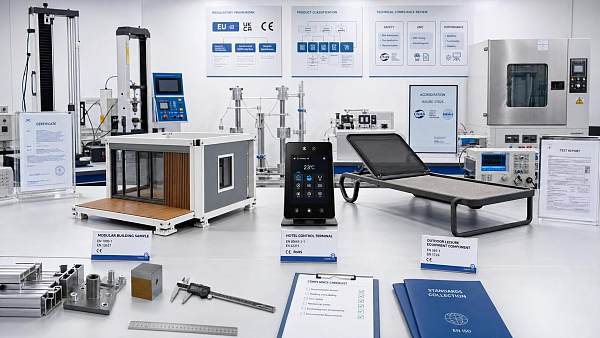
For organizations evaluating technical assets, the real risk is often hidden behind polished product narratives. Verified performance data, standards alignment, and traceable compliance evidence matter more than claims alone.
That is why data-led review models, such as those used by TerraVista Metrics, are increasingly valuable in tourism infrastructure and hospitality ecosystems.
The core elements that make the framework usable
Regulatory inventory and scope
The first requirement is a current inventory of obligations. This should separate mandatory law, contractual requirements, certification standards, and internal policy commitments.
Without that distinction, teams often over-control low-risk areas and miss critical ones.
Roles, authority, and accountability
A regulatory compliance framework fails quickly when ownership is vague. Each requirement needs a named control owner, a reviewer, and an escalation route.
This is especially important where engineering, operations, legal, procurement, and IT all touch the same risk.
Control design and evidence
Policies alone do not prove compliance. Auditors and counterparties look for evidence that controls are designed, operating, and reviewed.
Examples include inspection records, supplier declarations, testing reports, maintenance schedules, cybersecurity logs, and training completion data.
Monitoring and change management
Regulations change, and so do products, sites, and suppliers. A static framework goes out of date fast.
The better model includes periodic review, change triggers, and a method for updating controls when standards or operating conditions shift.
Where compliance gaps usually appear
Many organizations do not lack good intentions. They lack visibility between departments, documents, and physical assets.
Common gaps tend to appear in repeatable patterns:
- Requirements are tracked in spreadsheets with no single source of truth.
- Supplier certifications are collected once, then never revalidated.
- Operational changes occur without a compliance impact review.
- Evidence exists, but is fragmented across email, shared drives, and local files.
- Technical claims are accepted without benchmarked testing or independent verification.
- Cross-border procurement ignores differences in local approval rules or import controls.
These gaps become more serious in sectors that combine public safety, sustainability commitments, and capital-intensive assets.
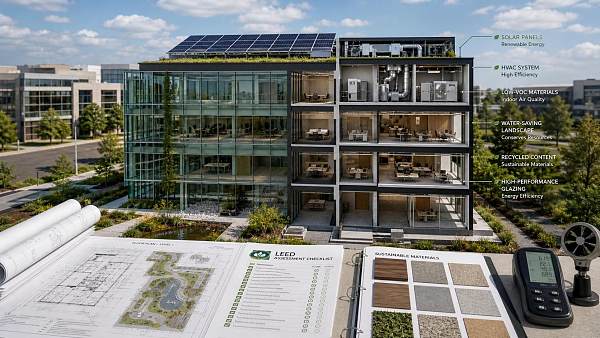
For example, a modular eco-structure may satisfy design expectations yet fail local thermal, fire, or carbon reporting obligations if the review stops at vendor brochures.
How the framework applies across tourism-linked assets
The same regulatory compliance framework can support very different asset categories, but the control focus will change by use case.
This cross-sector view matters because a single destination can contain all five categories. A fragmented approach usually creates blind spots at the interfaces.
What audit readiness looks like in practice
Audit readiness is not about producing documents at the last minute. It is the ability to show, with minimal disruption, that obligations are understood and controls are operating.
A well-prepared organization can answer five questions quickly:
- Which regulations and standards apply to this asset or activity?
- Who owns each control?
- What evidence proves performance?
- Where are current gaps, exceptions, or expired approvals?
- How are corrective actions tracked and closed?
The quality of evidence matters as much as the quantity. Verified reports, test results, and structured compliance analysis usually carry more weight than informal assurances.
This is one reason independent benchmarking and technical review can strengthen audit readiness. They provide an external reference point when internal assumptions are too optimistic.
A practical way to strengthen the framework
Improvement does not always require a large transformation program. Usually, the first gains come from sharper structure and better evidence discipline.
Start with critical assets
Focus first on assets tied to safety, guest experience, energy performance, data exposure, or heavy capital outlay.
Map supplier claims to proof
Do not stop at declarations. Match every major claim to a standard, test result, inspection record, or independent assessment.
Review cross-border assumptions
Imported compliance does not automatically equal local compliance. Confirm equivalence, acceptance, and any site-specific approvals.
Treat evidence as an operating asset
Store records in a way that supports retrieval, review cycles, expiry tracking, and corrective action follow-up.
Test the framework before the audit
Run a mock review on a live project, not just on policy documents. That exposes missing links between field activity and documented control.
From compliance burden to decision advantage
The best regulatory compliance framework does more than prevent failure. It improves procurement judgment, supports resilient design choices, and creates a clearer view of lifecycle risk.
For organizations developing future-facing tourism assets, that matters. The market increasingly rewards projects that can prove durability, interoperability, sustainability, and operational discipline.
The next step is usually straightforward: identify the highest-risk asset group, map applicable obligations, compare supplier claims with verified evidence, and test whether the current framework could withstand a real audit. That process often reveals where deeper benchmarking, technical validation, or regulatory analysis will have the greatest value.
Recommended News
 Sep 01, 2026How to Use a Tourism Standards Database to Verify Safety and Compliance RequirementsTourism standards database guide: verify safety, compliance, evidence scope, test conditions, and jurisdiction requirements with confidence.
 Aug 31, 2026Material Performance Validation: Tests and Acceptance Criteria for Critical PartsMaterial performance validation: discover essential tests and acceptance criteria that help critical parts withstand loads, corrosion, fatigue, and real-world service conditions.
 Aug 26, 2026What Is a CMS and How Do You Choose One for a Growing Business Website?CMS explained for growing business websites: learn how to choose a CMS that supports SEO, workflows, integrations, and long-term scalability without costly rebuilds.
 Aug 24, 2026How to Build a Technical Procurement Content Workflow for Faster Vendor EvaluationTechnical procurement content workflow strategies for faster vendor evaluation: standardize intake, compare evidence clearly, surface risks early, and cut costly procurement delays.
 Aug 20, 2026How to Evaluate Sustainable Concrete Alternatives for Low-Carbon Building ProjectsSustainable concrete alternatives: learn how to compare carbon data, structural performance, code compliance, and supply risk to choose low-carbon concrete solutions with confidence.
 Aug 17, 2026What Does Product Category Insights Reveal About Buyer Demand and Market Positioning?Product category insights reveal buyer demand, key product attributes, and market positioning. Learn how to spot reliable signals, compare segments, and make smarter decisions.
 Aug 13, 2026How to Use Industry Benchmarking to Improve Specification Planning DecisionsIndustry benchmarking for specification planning helps technical evaluators make smarter procurement decisions, reduce risk, and improve long-term performance with evidence-based standards.
 Aug 12, 2026Technical Certification Pricing Model: What Drives Cost and How to Compare QuotesTechnical certification pricing model explained: learn what drives cost, spot hidden risks in low quotes, and compare certification proposals with confidence before you approve budget.
 Aug 09, 2026How to Evaluate Tourism Equipment for Eco Resorts Without Compromising Guest ExperienceTourism equipment evaluation for eco resorts made practical: learn how to balance sustainability, durability, and guest comfort to avoid costly mistakes and choose smarter.
 Aug 07, 2026How to Evaluate LEED Standards for Environmental Sustainability in Building ProjectsEnvironmental sustainability assessment LEED standards explained: learn how to evaluate prerequisites, credits, costs, and project risks to achieve smarter, more reliable green building outcomes.
 Aug 05, 2026Why Eco Structures in the Middle East Are Shifting Toward Modular, Off-Grid DesignsEco structures in Middle East markets are moving to modular, off-grid designs for faster delivery, lower operating risk, and stronger climate resilience. Discover what is driving the shift.
 Jul 30, 2026Industry Insights for Market Expansion: How to Identify High-Potential Regions?Industry insights for market expansion: learn how to identify high-potential regions by assessing demand, infrastructure, compliance, and supply chain readiness for smarter growth.
 Jul 14, 2026How to Apply a Tourism Innovation Validation Framework to Assess New Visitor ProjectsTourism innovation validation framework explained: learn how to assess new visitor projects, reduce delivery risk, verify compliance, and make smarter investment decisions.
 Jul 13, 2026Import Market Research Checklist: How to Assess Demand, Tariffs, and Supplier RiskImport market research made practical: learn how to assess real demand, model tariffs, and reduce supplier risk with a clear checklist for smarter sourcing decisions.
 Jul 11, 2026Fade Resistant Durability: Which Test Methods Matter for Long-Term Outdoor Use?Fade resistant durability starts with the right test data. Discover which methods best predict long-term outdoor performance, color stability, and lower lifecycle risk.
 Jul 09, 2026Electronic Gadgets for Travel and Daily Use: How to Pick Features That MatterElectronic gadgets for travel and daily use should deliver real value. Learn how to compare battery life, portability, durability, and connectivity before you buy.
 Jul 08, 2026Regulatory Compliance Framework Explained: Core Elements, Gaps, and Audit ReadinessRegulatory compliance framework explained for modern organizations: learn core elements, common gaps, and audit readiness strategies to reduce risk, improve control, and strengthen decisions.
![]() Jul 07, 2026Faucets and Mixers Buying Guide: Types, Valve Options, and Finish SelectionFaucets and mixers buying guide covering fixture types, valve options, and finish selection. Compare durability, comfort, maintenance, and performance before you buy.
 Jul 06, 2026Tourism Equipment Specification Review: Which Ratings Matter Before You Buy?Tourism equipment specification review made practical: learn which ratings truly affect safety, lifecycle cost, compliance, and uptime before you choose a supplier.
 Jul 05, 2026What Is Material Fatigue in Composites? Failure Mechanisms and Service Life BasicsMaterial fatigue composites explained: learn key failure mechanisms, service life factors, and how to assess durability risks before specifying composite products.
 Jul 03, 2026Tourism Destination Infrastructure in North America: What Investors and Developers Evaluate FirstTourism destination infrastructure in North America shapes returns from day one. Discover what investors and developers assess first to reduce risk, improve resilience, and protect long-term value.
 Jul 02, 2026Tourism Development Validation Methodology Explained: Metrics, Data Sources, and Use CasesTourism development validation methodology explained with key metrics, trusted data sources, and real use cases to reduce risk, improve compliance, and guide smarter tourism investment decisions.
 Jun 30, 2026Regulatory Compliance Criteria Explained: How to Evaluate Requirements by Product and MarketRegulatory compliance criteria explained clearly: learn how to assess product and market requirements, reduce approval risk, and make smarter sourcing and market-entry decisions.
 Jun 29, 2026Efficient Procurement Planning: How to Reduce Delays and Control Budget RiskEfficient procurement planning helps reduce delays, control budget risk, and improve supplier decisions with data-driven strategies for stronger project delivery.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.