Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- How to Evaluate Spark Plug Suppliers for Consistent Quality and Lead TimesSpark plugs supplier evaluation guide: compare quality control, traceability, fitment, total cost, and reliable lead times to secure dependable engine maintenance supply.
- What Drives System Interoperability Testing Service Costs in Complex Projects?System interoperability testing service cost depends on integration scope, workflows, environments, and assurance needs. Learn how to budget smarter and reduce project risk.
- Project Planning Sourcing Guides: How to Qualify Suppliers Before Work StartsSourcing guides project planning helps teams qualify suppliers before work begins—verify compliance, delivery capacity, financial strength, and sustainability to reduce risk and protect project outcomes.
Popular Tags
TerraVista Metrics (TVM)Industry NewsRegulatory Compliance Procurement Support: How to Vet Suppliers Before Contract Award
auth.Time
Oct 07, 2026Click Count
Supplier compliance should be assessed before contract award, when the buyer still has leverage to request evidence, clarify responsibility, and compare alternatives. Once a supplier is selected, gaps in certification, product documentation, cybersecurity, environmental claims, or local approvals often become expensive change orders, delayed openings, or operational restrictions.
For procurement teams buying tourism infrastructure, hospitality technology, leisure equipment, furniture, or modular structures, regulatory compliance procurement support is therefore more than a document-collection exercise. It is a way to determine whether a supplier can deliver a legally usable, maintainable asset in the destination where it will operate. The question is not whether a supplier can present certificates. It is whether those certificates, test records, specifications, and operating controls apply to the exact product, project configuration, market, and contractual scope being purchased.
A sound pre-award review should focus on four matters: applicability, authenticity, delivery capability, and accountability after handover. Those areas expose most of the difference between a credible supplier and one that is merely prepared for a sales presentation.
Start with the asset and jurisdiction, not the supplier's certificate pack
Compliance requirements are determined by the intended use of an asset, its installation conditions, and the jurisdiction in which it will be placed into service. A certificate that is relevant to a residential product may not support use in a high-traffic hotel, attraction, public outdoor site, or commercial kitchen. Equally, evidence suitable for one export market may have little value in another.
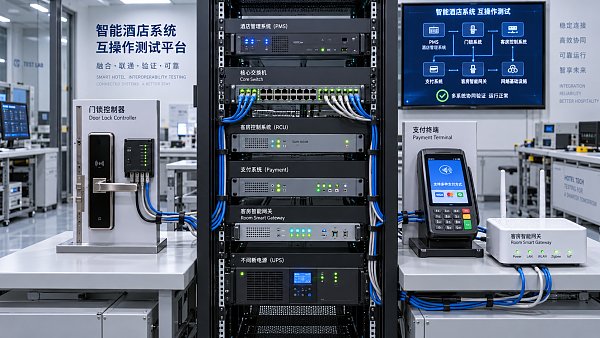
Procurement should first create an asset-specific compliance matrix. It does not need to be a lengthy legal register, but it should state what must be proven before award and what may be completed later under controlled conditions. For a prefabricated cabin, the matrix could address structural performance, fire behavior, thermal performance, electrical components, plumbing, transport limits, foundation interfaces, and local building approvals. For a smart hotel system, it may include electrical safety, wireless approvals, data protection obligations, network security expectations, accessibility, interoperability requirements, and records of software maintenance.
This framing prevents a common mistake: asking every bidder for the same generic set of certificates. A supplier of amusement hardware may need to demonstrate a different body of evidence from a supplier of hospitality furnishings, even where both are serving the same resort development. The purchase category should shape the review.
It is also important to separate three questions that are often collapsed into one:
- Does the product meet the relevant technical or regulatory requirement?
- Can the supplier lawfully sell, ship, install, or commission it in the destination market?
- Will the buyer receive the documents, approvals, training, and support needed to operate it compliantly?
A supplier can satisfy the first question while failing the second or third. For example, a product may have been tested to an appropriate standard, yet the supplier may lack a local installation partner, may not provide documentation in the required language, or may be unable to support the inspections required before public operation. Procurement should treat these as separate award criteria.
Validate evidence against the exact offer
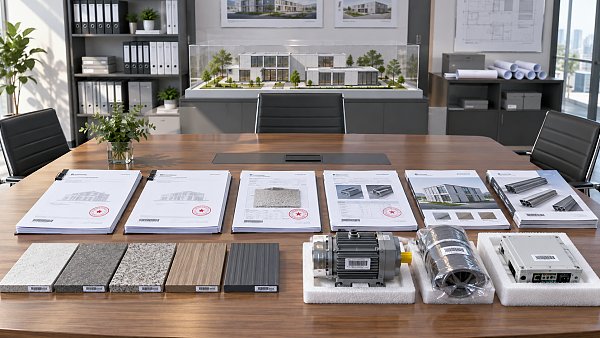
The most persuasive supplier submissions are usually organized, branded, and full of certificates. That presentation can conceal a basic mismatch between the evidence and the quoted product. Buyers should verify the connection between each document and the actual configuration in the commercial offer.
Begin with identity. Check the legal entity named on the certificate, test report, declaration, insurance policy, and quotation. A group company, factory affiliate, distributor, or former trading name may be legitimate, but the relationship should be clear. If the contracting supplier is not the certificate holder or manufacturer, the buyer needs a documented chain of authorization and a clear statement of who accepts technical responsibility.
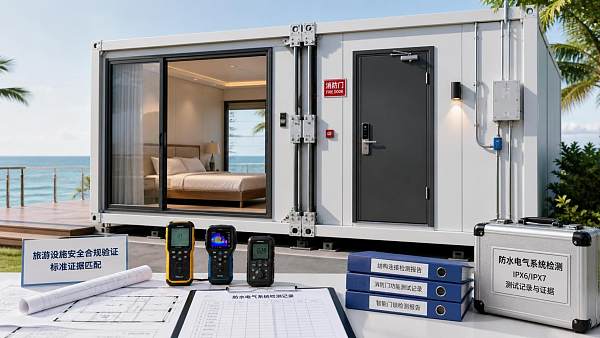
Then examine the product scope. Product names alone are not sufficient. Model numbers, revision levels, materials, component brands, load ratings, software versions, and manufacturing locations can all affect whether the evidence applies. A report for one seating frame does not automatically validate every finish, foam specification, fire treatment, or upholstery option. A test report for a standard modular unit may not cover site-specific modifications to glazing, roofing, HVAC equipment, electrical distribution, or snow and wind loading assumptions.
The same discipline applies to digital systems. A hotel platform may demonstrate security controls in its standard cloud deployment, while the proposed project uses an on-premises gateway, third-party lock integration, different data hosting arrangements, or a customized application layer. Procurement should ask which parts of the proposed architecture are covered by the evidence and where responsibility transfers to an integrator or site operator.
At minimum, each material compliance claim should be reviewed for:
- The issuing organization and whether it is appropriate for the claimed assessment.
- The supplier or manufacturer named in the document.
- The product family, model, configuration, and revision covered.
- The standard, regulation, or test method cited and its relevance to the destination market.
- The issue date, expiry date where applicable, and conditions or exclusions.
- The factory or production site covered when manufacturing location matters.
- The link between the submitted evidence and the bill of materials or technical schedule.
Copies without traceable references deserve further scrutiny. This does not mean every procurement team must become a certification authority. It means that unclear evidence should trigger a defined escalation path: a supplier clarification, independent technical review, direct confirmation with the issuer where practical, or a contract condition requiring verification before manufacture or shipment.
Do not confuse certification with production control
Even valid test evidence may say little about whether the supplier can reproduce the compliant product consistently. This distinction matters most where the purchase involves customized assemblies, high-volume furnishing packages, safety-critical leisure equipment, or products built across several factories.
A capable supplier can explain how approved designs are controlled from quotation to production. Buyers should look for a disciplined process around specifications, approved substitutions, incoming materials, manufacturing records, inspections, non-conformance handling, and final release. The level of detail should match the risk. A minor decorative accessory does not warrant the same review as a public-use climbing element, a fire-rated wall assembly, or a networked room-access system.
Questions that reveal production control are often more useful than broad requests for “quality certificates.” Ask who approves changes to a critical component, whether a substitute material can be introduced without buyer authorization, how serial numbers or batch records are maintained, and what happens when an inspection finds a deviation. Ask whether the supplier can provide a final documentation pack tied to the delivered units rather than a set of pre-contract marketing materials.
For long-life assets, the supply of compliant spare parts also belongs in the assessment. A ride control system, smart-room controller, modular building component, or specialist outdoor installation may require replacement parts years after the original delivery. A low initial price loses relevance if replacement parts are unavailable, incompatible with the original approval basis, or supplied without traceable specifications.
Review compliance as an operating risk, not only an entry requirement
Contract award is often driven by the need to begin construction, fit-out, or opening preparations. Yet regulatory exposure continues after delivery. The buyer should understand what must be maintained during the asset's operating life and which party performs that work.
For public-facing tourism assets, this may include inspection intervals, maintenance records, operator training, emergency procedures, calibration, software patching, incident reporting, accessibility adjustments, or documentation required for insurance and local authority review. Suppliers should be asked to identify their post-delivery obligations in specific terms. “Technical support available” is not an operating commitment.
Cybersecurity requires particular attention in hospitality technology procurement. A system that controls guest access, processes booking information, connects room devices, or interfaces with property-management software can create regulatory and operational exposure beyond the equipment purchase itself. The relevant diligence is not limited to a supplier's security policy. Buyers should establish how vulnerabilities are reported, how updates are delivered, whether updates can disrupt integrations, what data the supplier can access, where that data is processed, and what support remains available if the commercial relationship ends.
Environmental and sustainability claims should receive the same treatment. Procurement may need evidence related to material composition, restricted substances, lifecycle information, recyclability, sourcing, energy performance, or emissions associated with a particular asset. Broad statements such as “eco-friendly” or “sustainable design” should not be translated into contractual commitments unless the supplier has supplied measurable, product-specific substantiation. When a development has its own sustainability targets, those should be written into the technical schedule and matched to evidence requirements.
Use the tender process to expose gaps before negotiation narrows options
Many compliance problems arise because technical due diligence begins after commercial negotiations are largely complete. By that stage, the project team may be committed to a design, a delivery date, or an unusually low bid that depends on assumptions no one has tested.
A stronger approach places a small number of gating requirements early in the tender. Suppliers should be told which documents are mandatory at bid stage, which items require a project-specific compliance plan, and which gaps are disqualifying. This allows procurement to compare bids on a consistent basis and avoids giving an advantage to suppliers who answer vaguely.
Not every missing document should lead to rejection. Some approvals can only be completed after final design, local engineering review, mock-up testing, or site surveys. The issue is whether the remaining work is understood, budgeted, scheduled, and allocated to a responsible party. A supplier that identifies these dependencies clearly may be a lower-risk choice than one that claims blanket compliance without examining the project conditions.
Turn findings into contract controls
Due diligence loses value when findings remain in a procurement file rather than becoming enforceable obligations. The contract and technical schedules should reflect the matters that influenced supplier selection.
Useful controls are usually concrete. They can require delivery of named certificates and test reports, specify approved product configurations, prohibit material substitutions without written consent, define document language and format, require inspection access, and link payment milestones to satisfactory technical deliverables. For complex systems, acceptance criteria should include integration testing, commissioning records, training, access to maintenance tools, and confirmation that the final installed configuration matches the approved design.
Responsibility boundaries should also be written plainly. A supplier may be accountable for product conformity, while a local engineer is responsible for adapting the installation to site conditions and the owner is responsible for operational permits. Those divisions can be reasonable. They become risky when contract language leaves gaps between them, especially where a regulatory approval depends on inputs from several parties.
Procurement should avoid accepting broad disclaimers that quietly remove the value of the supplier's compliance statements. A limitation may be justified where the buyer controls design changes or installation. But it should not leave the supplier free to deliver a product that differs from the basis on which its evidence was assessed.
Apply more scrutiny where failure is hard to reverse
Compliance review should be proportionate, but it should not be evenly distributed. The highest level of scrutiny belongs to purchases where a late defect is difficult to replace, where public safety is involved, where regulatory approval controls project opening, or where an asset becomes deeply embedded in operations.
Examples include structural modules installed on remote sites, attractions used by the public, life-safety components, hotel systems connected to guest data and access control, and furnishing packages with required fire or material performance. In these categories, the cost of resolving an issue after installation can exceed the apparent saving achieved at tender.
Lower-risk purchases can use a lighter approach, provided the buyer still confirms product identity, basic legal suitability, and contractual responsibility. The objective is not to create paperwork for its own sake. It is to direct effort toward the evidence that protects capital expenditure, project schedules, and safe operation.
Before award, procurement should be able to state in plain language why the selected supplier is acceptable: which requirements apply, what evidence supports them, what remains to be completed, who owns each remaining action, and what happens if the evidence does not support delivery. When those answers are visible before the contract is signed, supplier selection becomes a defensible risk decision rather than a hopeful assumption.
Recommended News
 Oct 08, 2026What Drives System Interoperability Testing Service Costs in Complex Projects?System interoperability testing service cost depends on integration scope, workflows, environments, and assurance needs. Learn how to budget smarter and reduce project risk.
 Oct 03, 2026Verified Performance Certification: What It Proves During Product QualificationVerified performance certification helps teams qualify products with confidence. Learn how to assess scope, test conditions, and delivery controls before approval.
 Oct 01, 2026Multiaxial Material Fatigue Analysis for Predicting Service Life Under Variable LoadsMultiaxial material fatigue analysis helps predict service life under variable loads, enabling safer procurement, lower lifecycle risk, and durable tourism infrastructure.
 Sep 28, 2026What Does Tourism Destination Infrastructure Cost? A Budgeting Guide for DevelopersTourism destination infrastructure price guide for developers: budget utilities, systems, installation, lifecycle costs, and contingencies for smarter investments.
 Sep 26, 2026Regulatory Compliance Procurement Support: How to Vet Suppliers Before Contract AwardRegulatory compliance procurement support helps buyers vet suppliers, verify evidence, manage risks, and secure compliant assets before contract award.
 Sep 15, 2026System Integration Testing for Device Integration: Key Interfaces and Failure RisksSystem integration testing device integration: identify critical interfaces, hidden failure risks, recovery gaps, and acceptance evidence before connected devices go live.
 Sep 01, 2026How to Use a Tourism Standards Database to Verify Safety and Compliance RequirementsTourism standards database guide: verify safety, compliance, evidence scope, test conditions, and jurisdiction requirements with confidence.
 Aug 31, 2026Material Performance Validation: Tests and Acceptance Criteria for Critical PartsMaterial performance validation: discover essential tests and acceptance criteria that help critical parts withstand loads, corrosion, fatigue, and real-world service conditions.
 Aug 26, 2026What Is a CMS and How Do You Choose One for a Growing Business Website?CMS explained for growing business websites: learn how to choose a CMS that supports SEO, workflows, integrations, and long-term scalability without costly rebuilds.
 Aug 24, 2026How to Build a Technical Procurement Content Workflow for Faster Vendor EvaluationTechnical procurement content workflow strategies for faster vendor evaluation: standardize intake, compare evidence clearly, surface risks early, and cut costly procurement delays.
 Aug 20, 2026How to Evaluate Sustainable Concrete Alternatives for Low-Carbon Building ProjectsSustainable concrete alternatives: learn how to compare carbon data, structural performance, code compliance, and supply risk to choose low-carbon concrete solutions with confidence.
 Aug 17, 2026What Does Product Category Insights Reveal About Buyer Demand and Market Positioning?Product category insights reveal buyer demand, key product attributes, and market positioning. Learn how to spot reliable signals, compare segments, and make smarter decisions.
 Aug 13, 2026How to Use Industry Benchmarking to Improve Specification Planning DecisionsIndustry benchmarking for specification planning helps technical evaluators make smarter procurement decisions, reduce risk, and improve long-term performance with evidence-based standards.
 Aug 12, 2026Technical Certification Pricing Model: What Drives Cost and How to Compare QuotesTechnical certification pricing model explained: learn what drives cost, spot hidden risks in low quotes, and compare certification proposals with confidence before you approve budget.
 Aug 09, 2026How to Evaluate Tourism Equipment for Eco Resorts Without Compromising Guest ExperienceTourism equipment evaluation for eco resorts made practical: learn how to balance sustainability, durability, and guest comfort to avoid costly mistakes and choose smarter.
 Aug 07, 2026How to Evaluate LEED Standards for Environmental Sustainability in Building ProjectsEnvironmental sustainability assessment LEED standards explained: learn how to evaluate prerequisites, credits, costs, and project risks to achieve smarter, more reliable green building outcomes.
 Aug 05, 2026Why Eco Structures in the Middle East Are Shifting Toward Modular, Off-Grid DesignsEco structures in Middle East markets are moving to modular, off-grid designs for faster delivery, lower operating risk, and stronger climate resilience. Discover what is driving the shift.
 Jul 30, 2026Industry Insights for Market Expansion: How to Identify High-Potential Regions?Industry insights for market expansion: learn how to identify high-potential regions by assessing demand, infrastructure, compliance, and supply chain readiness for smarter growth.
 Jul 14, 2026How to Apply a Tourism Innovation Validation Framework to Assess New Visitor ProjectsTourism innovation validation framework explained: learn how to assess new visitor projects, reduce delivery risk, verify compliance, and make smarter investment decisions.
 Jul 13, 2026Import Market Research Checklist: How to Assess Demand, Tariffs, and Supplier RiskImport market research made practical: learn how to assess real demand, model tariffs, and reduce supplier risk with a clear checklist for smarter sourcing decisions.
 Jul 11, 2026Fade Resistant Durability: Which Test Methods Matter for Long-Term Outdoor Use?Fade resistant durability starts with the right test data. Discover which methods best predict long-term outdoor performance, color stability, and lower lifecycle risk.
 Jul 09, 2026Electronic Gadgets for Travel and Daily Use: How to Pick Features That MatterElectronic gadgets for travel and daily use should deliver real value. Learn how to compare battery life, portability, durability, and connectivity before you buy.
 Jul 08, 2026Regulatory Compliance Framework Explained: Core Elements, Gaps, and Audit ReadinessRegulatory compliance framework explained for modern organizations: learn core elements, common gaps, and audit readiness strategies to reduce risk, improve control, and strengthen decisions.
![]() Jul 07, 2026Faucets and Mixers Buying Guide: Types, Valve Options, and Finish SelectionFaucets and mixers buying guide covering fixture types, valve options, and finish selection. Compare durability, comfort, maintenance, and performance before you buy.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.