Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- What Engineering Performance Testing Should Cover During a Specification ReviewEngineering performance testing for specification review: learn how to verify structural strength, durability, safety, sustainability, and system reliability before costly project decisions.
- Planning Recreational Cable Transport Networks for Resorts and Mountain ParksExplore recreational cable transport networks for resorts and mountain parks, with expert planning insights on capacity, terrain, safety, station design, and long-term performance.
- How to Plan Theme Park Infrastructure for Mixed-Use DevelopmentsTheme park infrastructure for mixed use developments: plan resilient utilities, circulation, attractions, hospitality, and digital systems for scalable destinations.
Popular Tags
TerraVista Metrics (TVM)Industry NewsHow to Read a Compliance Standards Assessment Report for Supplier Approval
auth.Time
Sep 03, 2026Click Count
How should you approach a compliance standards assessment report before approving a supplier?
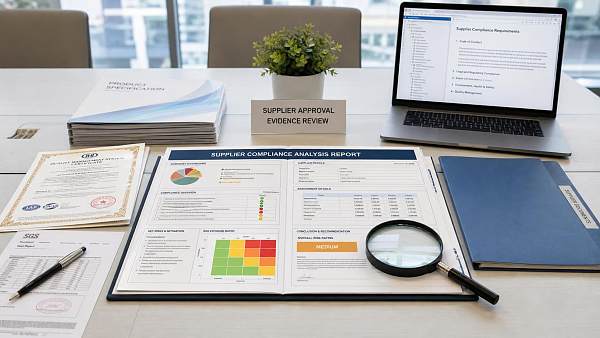
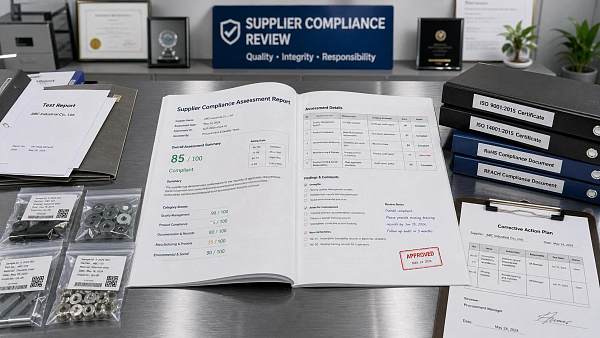
A compliance standards assessment report should be read as evidence, not decoration.
Its real value lies in showing whether a supplier can meet technical, regulatory, and operational expectations over time.
That matters even more in tourism-linked projects, where assets often combine engineering performance, safety, sustainability, and guest-facing reliability.
A modular cabin, hotel IoT platform, outdoor fixture, amusement component, or hospitality furnishing may all look acceptable at first glance.
The compliance standards assessment report tells you whether those claims survive measurable review.
In practical terms, the report helps separate marketing language from verified performance data.
That is why firms such as TerraVista Metrics frame compliance analysis as part of procurement intelligence, not just certification paperwork.
Before comparing prices or lead times, read the report for scope, testing basis, deviations, and evidence quality.
What does a compliance standards assessment report actually confirm?
It confirms how a product, system, or supplier was assessed against defined standards.
That sounds simple, but the depth can vary a lot.
Some reports cover full laboratory verification and factory controls.
Others only summarize document review or sample-based inspection.
A strong compliance standards assessment report usually answers five basic questions:
- Which standards or regulations were used as the benchmark.
- What exact product, model, batch, or process was assessed.
- How the assessment was performed and by whom.
- Whether the result was compliant, conditional, or nonconforming.
- What limitations, exceptions, or unresolved issues remain.
If any of those points are unclear, the report is harder to rely on for supplier approval.
In actual sourcing reviews, weak scope definition causes many bad decisions.
For example, a report may verify fire resistance for one structure configuration, but not for the customized version being quoted.
The label looks reassuring, yet the approved item may fall outside the tested boundary.
Which sections deserve the closest attention when you read the report?
Start with the front page, but do not stop there.
Executive conclusions are useful, although the real risk usually sits in the detail pages.
The sections below usually carry the most decision value.
A good reading habit is to move from scope to methodology, then to findings, and only then to the final conclusion.
This order keeps the compliance standards assessment report in context.
Otherwise, it is easy to overvalue a clean summary page.
When does a “compliant” result still require caution?
Quite often, actually.
A compliant outcome does not always mean low procurement risk.
It only means the assessed item met the stated criteria within the stated limits.
The more useful question is whether those limits match your real operating conditions.
Take a smart hotel system as an example.
A compliance standards assessment report may confirm cybersecurity controls for one integration environment.
If your site uses different third-party platforms, the practical risk changes.
The same applies to eco-structures, outdoor gear, or attraction hardware exposed to heavier traffic or harsher climates.
Watch for these caution signals:
- The report is based on prototype samples only.
- Factory audit findings remain open or partially closed.
- Critical components were substituted after testing.
- Local regulations differ from the cited international standard.
- The report excludes installation, maintenance, or software updates.
In other words, read the compliance standards assessment report together with the intended application.
That is usually the difference between formal compliance and dependable approval.
How can you compare two suppliers without getting lost in paperwork?
The easiest mistake is comparing report thickness instead of evidence quality.
A longer compliance standards assessment report is not automatically a stronger one.
What helps more is a side-by-side review based on comparable decision points.
Use the same questions for each supplier, even when the report formats differ.
A practical comparison checklist
- Does each compliance standards assessment report cover the same standard edition?
- Were tests completed by equivalent laboratories or assessment bodies?
- Are nonconformities clearly rated by severity and closure status?
- Do the reports include supply chain controls, not only product tests?
- Is there evidence of repeatability across batches, sites, or software versions?
This approach is especially useful across mixed tourism assets.
A glamping structure may require structural and carbon compliance review.
A furnishing supplier may need wear resistance, material safety, and sustainability verification.
An amusement equipment source may depend more heavily on fatigue testing and ongoing maintenance compliance.
The principle stays the same: compare relevance, rigor, and residual risk.
This is where data-led review frameworks, like those used by technical benchmarking groups, become more useful than a simple pass-fail file check.
What are the most common mistakes when reading a compliance standards assessment report?
Most mistakes come from reading too fast or trusting labels too much.
Here are the ones that create the most trouble later.
- Treating certification marks as proof of current operational conformity.
- Ignoring annexes, where exclusions and technical assumptions often sit.
- Missing the difference between product compliance and supplier process compliance.
- Assuming one region’s standard automatically satisfies another region’s rules.
- Overlooking corrective action deadlines and surveillance requirements.
Another frequent issue is failing to connect the report to total project risk.
A narrow technical gap can still create cost, delay, or warranty exposure.
For tourism infrastructure, that exposure may affect guest safety, uptime, energy use, or brand trust.
So the compliance standards assessment report should never be reviewed in isolation.
It works best when paired with delivery records, maintenance obligations, and change-control history.
What is the best next step after reading the report?
Turn the document into a decision map.
Highlight what is verified, what is conditional, and what still needs confirmation.
That keeps supplier approval grounded in evidence rather than assumption.
A useful next-step sequence looks like this:
- Match the report scope to your actual product, site, or deployment condition.
- List every limitation, exception, and open corrective action.
- Check whether local regulatory requirements add extra approval steps.
- Compare findings against at least one alternative supplier.
- Record approval conditions for future audits, reorders, and specification changes.
The strongest procurement decisions usually come from this kind of structured reading.
A compliance standards assessment report is not just a gatekeeping form.
It is a way to judge durability, technical fit, and compliance resilience before problems appear on site.
If the document leaves important questions open, treat that gap as part of the risk picture.
Then build the next review around evidence, operating context, and long-term performance, not just a compliant label.
Recommended News
 Aug 28, 2026What Do Standardized Performance Benchmarks Cost, and What Do Buyers Get?Standardized performance benchmarks price explained: compare costs, scope, and buyer deliverables to reduce procurement risk and make confident investment decisions.
 Aug 03, 2026How to Read a Compliance Analysis Report Before Supplier ApprovalCompliance analysis report guide: learn how to verify scope, evidence, exclusions, and risk before supplier approval, helping you avoid costly compliance gaps and make smarter sourcing decisions.
 Aug 02, 2026What Should Executives Look for in a Market Intelligence Report Dashboard?Market intelligence report dashboard essentials for executives: learn how to spot decision-ready insights, benchmark risk, source confidence, and business impact before making high-stakes moves.
 Jul 29, 2026Recreational Cable Transport Global Market: Key Growth Drivers and Regional OutlookRecreational cable transport global market analysis explores key growth drivers, regional outlook, technology shifts, and investment risks shaping future leisure mobility opportunities.
 Jul 26, 2026Tourism Development Report: Key Market Signals, Investment Priorities, and Growth RisksTourism development report on market signals, investment priorities, and growth risks—discover where tourism assets can deliver resilient returns, sustainability value, and smarter expansion.
 Jul 25, 2026How to Evaluate a Standardized Performance Benchmarks Research Firm?Standardized performance benchmarks research firm selection starts with method, independence, and industry fit. Learn how to compare firms and choose evidence that supports smarter procurement decisions.
 Jul 18, 2026How to Read a Prefab Durability Testing Report Before Specifying Modular UnitsPrefab durability testing report essentials: learn how to assess test scope, standards, margins, and hidden risks before specifying modular units with confidence.
 Jul 15, 2026How a Market Intelligence Agency Supports Supplier Screening and Market Entry DecisionsA market intelligence agency helps businesses screen suppliers, reduce entry risk, and make smarter market decisions with verified data, compliance insight, and actionable analysis.
 Jul 14, 2026Project Planning Intelligence Tools: Which Features Matter for Cross-Functional Teams?Project planning intelligence tools for cross-functional teams: discover the must-have features for risk, compliance, forecasting, and smarter project decisions.
 Jul 13, 2026Tourism Equipment Market Evaluation: Which Demand, Price, and Channel Metrics Matter?Tourism equipment market evaluation reveals which demand, price, and channel metrics truly drive margins, reduce risk, and improve procurement decisions across modern tourism projects.
 Jul 11, 2026Compliance Analysis USA: How to Review Testing and Documentation Before BuyingCompliance analysis USA made practical: learn how to verify test reports, certification scope, and documentation before buying to reduce sourcing risk, control costs, and choose suppliers with confidence.
 Jul 10, 2026How to Compare Product Category Market Price Across Suppliers Without Missing Hidden CostProduct category market price comparison goes beyond the lowest quote. Learn how to uncover hidden costs across suppliers and make smarter, lower-risk buying decisions.
 Jul 08, 2026Presentation Tools Compared: Which Features Matter for Team Training and Demos?Presentation tools compared for team training and demos: discover which features improve collaboration, technical clarity, and reliable delivery across real operational workflows.
![]() Jul 07, 2026Tourism Supply Chain Analysis in North America: Key Cost Drivers and BottlenecksTourism supply chain analysis North America reveals key cost drivers, freight risks, compliance pressure, and integration bottlenecks—helping tourism projects cut risk and make smarter investment decisions.
 Jul 03, 2026On Site Thermal Efficiency Testing: When It’s Required and Which Metrics Matter MostOn site thermal efficiency testing reveals how buildings perform in real conditions. Learn when it’s required, which metrics matter most, and how to reduce energy risk.
 Jul 02, 2026What Drives Industry Reports Cost Factors: Data Scope, Method, and Update FrequencyIndustry reports cost factors explained: see how data scope, research method, and update frequency shape report value, pricing, and smarter investment decisions.
 Jun 30, 2026Fashion Trends 2026: Which Materials, Silhouettes, and Colors Are Shaping New Collections?Fashion trends 2026 reveal the materials, silhouettes, and colors shaping scalable new collections. Discover buyer-ready insights on comfort, utility, and strategic color direction.
 Jun 27, 2026Tourism Asset Evaluation Cost Factors: What Drives Valuation in Resort Projects?Tourism asset evaluation cost factors shape resort valuation through site complexity, compliance, smart systems, and lifecycle risk. See what really drives cost and stronger investment decisions.
 Jun 25, 2026How to Use Material Sustainability Analysis in Product Selection and Supplier EvaluationMaterial sustainability analysis helps buyers compare real lifecycle value, durability, compliance, and supplier reliability. Learn how to make smarter product selection decisions.
 Jun 21, 2026Tourism Carbon Metrics: How Hotels and Destinations Measure Emissions in PracticeTourism carbon in practice: learn how hotels and destinations measure emissions, set clear boundaries, compare assets fairly, and turn data into credible low-carbon decisions.
 Jun 20, 2026What Affects Outdoor Furniture Price? Materials, Durability, MOQ, and Shipping CostsOutdoor furniture price depends on more than design. Explore how materials, durability, MOQ, customization, and shipping costs shape real project value and smarter buying decisions.
 Jun 19, 2026How to Read a Compliance Standards Assessment Report for Supplier ApprovalCompliance standards assessment report guide for smarter supplier approval. Learn how to verify scope, findings, risks, and evidence quality before you commit.
 Jun 14, 2026Emerging Markets Outlook: 5 Supply Chain Shifts Reshaping Global SourcingEmerging markets are reshaping global sourcing through resilience, compliance, smart manufacturing, sustainability, and category-specific insight. Discover 5 shifts buyers can’t ignore.
 Jun 13, 2026Export Import Compliance Checklist: Key Documents, HS Codes, Duties, and Common DelaysExport import compliance checklist covering key documents, HS codes, duties, and common delay risks. Learn how to reduce customs issues, control landed cost, and keep shipments moving.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.