Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- How to Evaluate Spark Plug Suppliers for Consistent Quality and Lead TimesSpark plugs supplier evaluation guide: compare quality control, traceability, fitment, total cost, and reliable lead times to secure dependable engine maintenance supply.
- What Drives System Interoperability Testing Service Costs in Complex Projects?System interoperability testing service cost depends on integration scope, workflows, environments, and assurance needs. Learn how to budget smarter and reduce project risk.
- Project Planning Sourcing Guides: How to Qualify Suppliers Before Work StartsSourcing guides project planning helps teams qualify suppliers before work begins—verify compliance, delivery capacity, financial strength, and sustainability to reduce risk and protect project outcomes.
Popular Tags
TerraVista Metrics (TVM)Industry NewsSingapore MSA Enforces CyberTrust Plus for Yacht Tech OTA Firmware
auth.Dr. Hideo Tanaka (Outdoor Gear Engineering Lead)Time
Oct 07, 2026Click Count
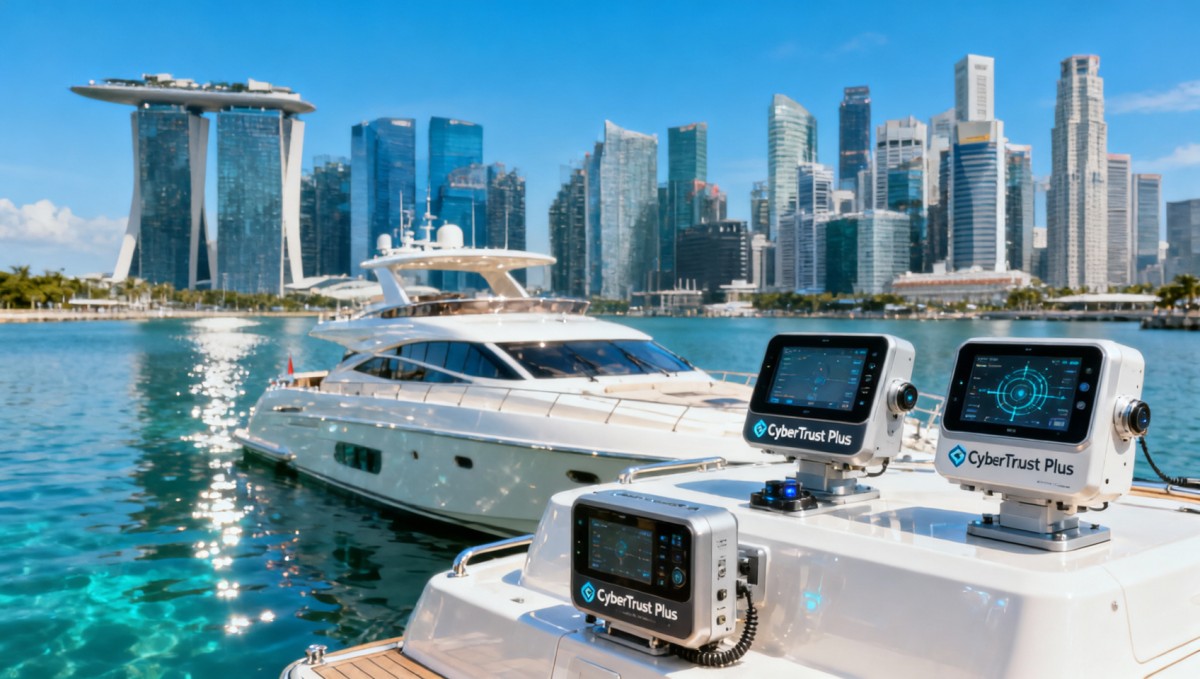
Starting 1 June 2026, the Maritime and Port Authority of Singapore (MPA)’s Marine Safety Agency (MSA) will require all yacht technology devices — including navigation, remote monitoring, and energy management modules — operating in Singaporean waters to hold CyberTrust Plus certification. This mandate directly affects marine electronics manufacturers, aftermarket service providers, and system integrators serving the Asia-Pacific superyacht and retrofit markets.
Event Overview
On 5 May 2026, Singapore’s Marine Safety Agency (MSA), under the Maritime and Port Authority of Singapore (MPA), announced that, effective 1 June 2026, all Yacht Tech devices installed on yachts entering Singapore waters must be certified under the CyberTrust Plus framework. The certification specifically assesses over-the-air (OTA) firmware signature integrity, vendor-defined vulnerability response service-level agreements (SLAs), and capability for localized logging retention. Chinese vendors without this certification are explicitly excluded from bidding on yacht retrofit and maintenance projects in Singapore.
Industries Affected
Marine Electronics Manufacturers (OEMs & Tier-2 Suppliers)
Manufacturers producing navigation systems, vessel monitoring units, or onboard energy controllers face direct compliance pressure. Non-certified devices cannot be legally deployed on yachts operating in Singapore waters — limiting market access even if physical import remains unrestricted. Impact manifests as lost tender eligibility, delayed project timelines, and potential rework costs for existing installations.
Yacht Retrofit & Maintenance Service Providers
Companies offering installation, upgrade, or after-sales support for yacht tech systems must now verify CyberTrust Plus status before quoting or deploying equipment. Uncertified hardware may invalidate service contracts or trigger non-compliance penalties during port state control checks. This introduces new verification steps in procurement workflows and increases technical due diligence overhead.
Systems Integrators & Marine IT Solution Providers
Firms bundling third-party hardware into unified marine management platforms must ensure each component meets the certification requirement. Integration testing now includes validation of signed OTA update chains and local log storage architecture — adding complexity to solution design and documentation requirements for Singapore-bound deployments.
What Enterprises and Practitioners Should Monitor and Do Now
Track official CyberTrust Plus implementation guidance
The MSA has not yet published full technical criteria, test lab accreditation lists, or application timelines for certification renewal. Companies should monitor MPA’s official portal and CyberTrust Plus program updates for clarity on audit scope, evidence submission formats, and validity periods.
Assess current product portfolio against three core requirements
Focus evaluation on: (1) cryptographic signing of all OTA firmware updates; (2) documented SLA commitments for critical vulnerability remediation (e.g., ≤72-hour acknowledgment, ≤14-day patch availability); and (3) ability to retain device-generated logs locally — without mandatory cloud relay or offshore transmission. Prioritize devices used in Singapore-flagged or Singapore-berthed vessels.
Distinguish policy signal from operational enforcement
This is a regulatory entry condition, not a voluntary standard. As of 1 June 2026, absence of CyberTrust Plus certification means contractual ineligibility — not merely reputational risk. Tender documents issued by Singapore-based marinas, yacht management firms, or government-linked operators will now include explicit certification clauses.
Prepare documentation and cross-functional alignment early
Engineering, compliance, and sales teams should jointly map firmware update architectures and log retention logic. Begin internal gap analysis using publicly available CyberTrust Plus high-level principles. Where certification is pending, draft transitional statements for client communications — noting expected timeline and interim mitigation measures (e.g., manual update protocols, on-device log export).
Editorial Perspective / Industry Observation
Observably, this requirement signals Singapore’s shift from general cybersecurity awareness to enforceable, device-level accountability in maritime digital infrastructure. It is not merely a procurement preference but a jurisdictional access control mechanism tied to operational legality in sovereign waters. Analysis shows that while CyberTrust Plus was previously referenced in advisory contexts, its elevation to a mandatory, binary gatekeeper credential marks a structural tightening — particularly for non-local vendors relying on legacy certification pathways. From an industry perspective, this reflects growing convergence between maritime safety regulation and embedded systems security governance. Current enforcement appears targeted and scoped, but sustained attention is warranted as similar frameworks emerge in other ASEAN ports with aligned digital trust agendas.
Conclusion
This mandate establishes CyberTrust Plus not as a best-practice benchmark but as a de facto licensing prerequisite for yacht technology deployment in Singapore. Its significance lies less in novelty and more in enforceability: it transforms cybersecurity assurance from a technical feature into a contractual and regulatory precondition. For stakeholders, it is more appropriately understood as an operational compliance threshold than a strategic initiative — one requiring concrete technical alignment, not just policy endorsement.Information Source
Primary source: Official announcement by the Marine Safety Agency (MSA), Maritime and Port Authority of Singapore (MPA), dated 5 May 2026.
Note: Certification test procedures, accredited laboratories, and renewal mechanisms remain pending public release and are subject to ongoing observation.Recommended News
 Oct 02, 2026North American Yacht Tech: Market Shifts Reshaping Retrofit and New-Build DemandYacht tech North America is reshaping retrofit and new-build choices. Explore smarter energy, connectivity, cybersecurity, and lifecycle strategies for lasting yacht value.
 Aug 19, 2026What Does a Marine Hospitality Consultant Do for Cruise and Yacht Projects?Marine hospitality consultant expertise helps cruise and yacht projects avoid costly design and procurement mistakes, improve guest experience, and build commercially viable onboard spaces.
 Jul 15, 2026Yacht Tech Components Buying Guide: How to Evaluate Compatibility, Durability, and Lead TimeYacht tech components buying guide: learn how to assess compatibility, durability, and lead time to reduce downtime, control hidden costs, and choose suppliers with confidence.
 Jul 15, 2026What Is Digital Marine Hospitality Technology and Which Guest Services Does It Improve?Digital marine hospitality technology improves boarding, cabin access, dining, entertainment, and safety at sea. Learn how smart marine systems boost guest experience and operational performance.
 Jul 12, 2026Saudi SASO Expands Yacht Tech Rules for Smart AnchoringSaudi SASO expands Yacht Tech rules for smart anchoring, adding SABER certification and local cloud logging requirements. Learn key deadlines, firmware upgrade steps, and export risks before October 1.
 Jul 11, 2026UAE Decree 12 Sets LDOM Rule for Imported YachtsUAE Decree 12 sets the LDOM rule for imported yachts from Sept 2026. Learn how the new Local Data Sovereignty Module requirement impacts compliance, delivery, retrofits, and sourcing.
![]() Jul 07, 2026How Yacht Technology in the Middle East Is Shaping Smart Marinas and Onboard SystemsYacht technology Middle East is driving smarter marinas, connected onboard systems, and energy-ready waterfronts. Discover what investors and operators should watch next.
 Jul 04, 2026Suez Canal Tightens Yacht Tech Clearance RulesSuez Canal yacht tech clearance rules tighten from July 3, 2026. Learn how new 72-hour disclosure and approved-list requirements may impact exporters, integrators, logistics, and buyers.
 Jul 03, 2026Suez Canal Adds Tech Whitelist for Yacht Tech CargoSuez Canal Yacht Tech cargo rules now hinge on a tech whitelist. Learn which device models face 18-day delays, what the new clearance means, and how to protect shipping timelines.
 Jul 02, 2026Suez Canal Tightens Yacht Tech Transit ChecksSuez Canal Tightens Yacht Tech Transit Checks: learn how the new whitelist, certification filing, and firmware hash rules may delay shipments and raise costs for yacht tech suppliers.
 Jul 01, 2026Suez Canal Adds Tech Whitelist for Yacht EquipmentSuez Canal tech whitelist now affects yacht equipment transit. Learn how SCA-approved models, EMC/IPX8 verification, and delivery planning impact exporters, buyers, and marine tech suppliers.
 Jun 24, 2026Engineering Performance Testing for Marine Grade Materials: Key Metrics and Failure RisksEngineering performance testing marine grade materials helps uncover corrosion, fatigue, and coating risks before failure. Learn the key metrics that protect coastal assets, uptime, and long-term value.
 Jun 14, 2026How to Evaluate a Yacht Tech Supplier for Navigation, Power, and Onboard SystemsYacht Tech supplier evaluation made simple: learn how to compare navigation, power, and onboard systems for compliance, integration, reliability, and lower long-term risk.
![]() Jun 09, 2026How to Evaluate a Yacht Tech Supplier: Certifications, Lead Times, and After-Sales SupportYacht Tech supplier evaluation starts with proof, not promises. Learn how certifications, lead times, and after-sales support reveal risk, reliability, and long-term value.
 May 22, 20262026 Shanghai Yacht Show Closes; Chinese Suppliers Invited for Middle East Factory Audits2026 Shanghai Yacht Show closed — Chinese marine tech suppliers invited for Middle East factory audits. Act now to meet ISO 8846 & IP67 deadlines!
 May 21, 20262026 Shanghai Yacht Show Closes: Yacht Tech Suppliers Receive Factory Audit Invitations from Middle East OwnersYacht Tech suppliers: 37 factory audit invites from UAE, KSA & Qatar at 2026 Shanghai Yacht Show — verify ISO 8846 & DNV GL compliance now!
 May 20, 20262026 Shanghai Yacht Show Closes; Chinese Suppliers Invited for Middle East Factory Audits2026 Shanghai Yacht Show closed — Chinese yacht tech suppliers invited to Middle East factory audits under Yacht Tech initiative. Act now to meet DNV GL, LR & ASME BPVC requirements.
 May 20, 20262026 Shanghai Yacht Show Closes; Chinese Yacht Tech Suppliers Invited to Middle East FactoriesChinese yacht tech suppliers invited to Middle East factories after 2026 Shanghai Yacht Show — seize audit opportunities in smart outboards, carbon decks & AI marine security.
 May 19, 20262026 Shanghai Yacht Show Closes: Chinese Yacht Tech Suppliers Invited for Middle East Factory AuditsChinese yacht tech suppliers: Act now! Middle East buyers invite factory audits by June 2026 — ISO 8846:2025 & DNV-GL SE-0022 compliance required.
 May 18, 20262026 Shanghai Yacht Show Closes: Chinese Yacht Tech Suppliers Receive Factory Audit Invitations from Middle East OperatorsYacht Tech suppliers: 7 Chinese firms invited to Middle East factory audits after 2026 Shanghai Yacht Show—boost global credibility & unlock Gulf market access now.
 May 17, 20262026 Shanghai Yacht Show Closes with Middle East Shipowners Inviting Chinese Suppliers for Joint Factory Audits2026 Shanghai Yacht Show: Middle East shipowners invite Chinese suppliers for joint factory audits—act now to meet ISO 8846:2023 & DNV GL requirements.
 May 16, 20262026 Shanghai Yacht Show Closes; Chinese Yacht Tech Suppliers Invited to Mid-East Factory AuditsChinese yacht tech suppliers invited to Mid-East factory audits after 2026 Shanghai Yacht Show — seize this strategic gateway to $2.4B regional modernization projects.
 May 15, 20262026 Shanghai Yacht Show Closes with Middle East Factory Audits for Chinese Suppliers2026 Shanghai Yacht Show sparks Middle East factory audits for Chinese yacht tech suppliers — seize cross-border procurement opportunities now.
 May 14, 20262026 Shanghai International Yacht Show Closes with Middle East Shipowners Inviting Chinese Yacht Tech Suppliers for Joint Factory Audits2026 Shanghai International Yacht Show: Middle East shipowners invite Chinese yacht tech suppliers for joint factory audits—smart motors, carbon fiber decks & AI energy systems.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.