Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- Hotel Security Protocols: A Compliance Checklist for Protecting Guests and StaffSecurity protocols for hospitality: use this practical hotel compliance checklist to protect guests, staff, data, access points, and emergency operations.
- How to Evaluate Resort Slide System Suppliers for Safety, Capacity, and Project SupportResort slide systems supplier evaluation guide: compare safety evidence, real capacity, durable materials, and project support for confident resort investments.
- Sustainable Building Materials Pricing: How Buyers Compare Cost, Life Cycle, and RiskSustainable building materials pricing explained: compare installed cost, life-cycle value, carbon evidence, and supply-chain risk for smarter procurement decisions.
Popular Tags
TerraVista Metrics (TVM)Industry NewsEU Draft Rules: Kiosk & Guestroom Tech Require Dual GDPR + EN 301 549 V3.2.1 Certification
auth.Lydia Vancini (Smart Hospitality IoT Consultant)Time
Sep 09, 2026Click Count
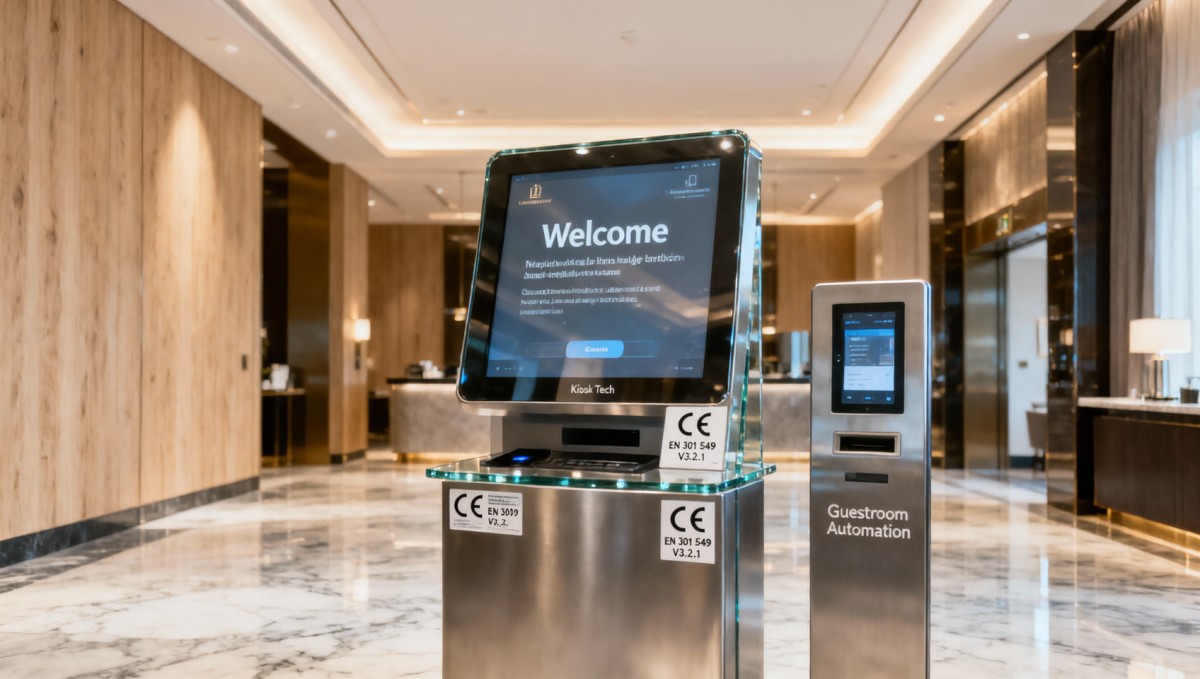
On 23 May 2026, the European Commission formally submitted the draft Digital Services Infrastructure Compliance Amendment to EU Member States, mandating that all interactive kiosks (Kiosk Tech) and guestroom automation systems deployed in public venues—including hotels, airports, and exhibition centres—must comply with both the GDPR’s data localisation requirements and the updated accessibility standard EN 301 549 V3.2.1 starting 1 January 2027. Exporters from China—and other third countries—supplying such systems to the EU will lose eligibility for EU public procurement contracts and major hotel chain tenders if they fail to achieve dual certification ahead of the deadline.
Event Overview
The European Commission published the draft Digital Services Infrastructure Compliance Amendment on 23 May 2026. The draft requires Kiosk Tech and Guestroom Automation systems intended for deployment in publicly accessible locations across the EU to meet two concurrent compliance benchmarks by 1 January 2027: (i) GDPR-compliant data localisation (including storage and processing within the EEA), and (ii) conformance with EN 301 549 V3.2.1—the latest harmonised European standard for ICT accessibility. The draft is currently under review by Member States; no final adoption date or formal entry-into-force timeline has been announced.
Which Subsectors Are Affected
Direct Exporters (Hardware & System Integrators)
Companies exporting Kiosk Tech or Guestroom Automation hardware, firmware, or integrated solutions to the EU are directly subject to the requirement. Non-compliance will result in exclusion from EU public procurement frameworks and pre-qualified vendor lists used by multinational hotel groups (e.g., Accor, Marriott, IHG). Certification must cover full system architecture—not just individual components—making retrofitting existing products technically and commercially challenging.
Embedded Software & Firmware Providers
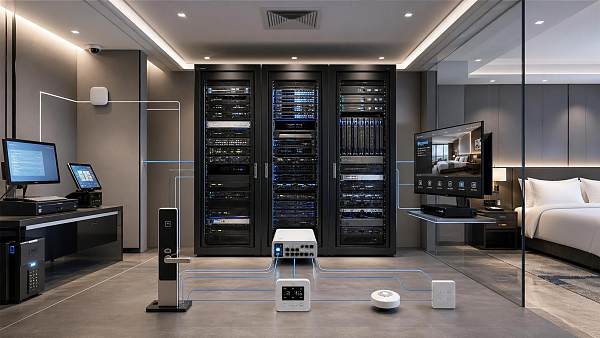
Suppliers of operating systems, access control modules, voice interface engines, or cloud-connected management platforms embedded in kiosks or room automation systems may face upstream compliance demands. If their software processes personal data or affects accessibility functionality (e.g., screen reader support, contrast settings, navigation logic), it falls within the scope of both GDPR data handling rules and EN 301 549 V3.2.1 conformance testing—even when supplied as a B2B component.
EU-Based Distributors & Resellers
Distributors and value-added resellers placing these systems on the EU market bear legal responsibility under the EU’s Market Surveillance Regulation (Regulation (EU) 2019/1020). They must verify and retain technical documentation demonstrating dual certification before placing devices on the market. Absent valid conformity evidence, they risk enforcement actions—including product withdrawal and liability for non-compliant deployments.
What Relevant Enterprises or Practitioners Should Focus On — And How to Respond Now
Monitor official status of the draft amendment and national transposition timelines
The draft remains subject to intergovernmental consultation and possible revision. Enterprises should track updates via the Official Journal of the European Union and national market surveillance authorities (e.g., Germany’s BAFA, France’s DGCCRF). Final adoption is not guaranteed before end-2026, and transitional periods—if introduced—will only be confirmed upon publication of the adopted text.
Prioritise certification for high-volume, EU-targeted SKUs—not entire portfolios
Given resource constraints, companies should identify specific kiosk models or automation platform versions already qualified for EU hotel or airport tenders. These SKUs should be prioritised for dual certification. Avoid broad-spectrum testing; instead, align test scope with actual use cases (e.g., check-in kiosks with biometric capture require stricter GDPR data flow mapping than basic information displays).
Distinguish between regulatory signal and enforceable obligation
As of now, the requirement exists only as a draft proposal. No penalties, audits, or mandatory certification schemes are yet active. However, leading EU procurement bodies and hotel chains are already referencing EN 301 549 V3.2.1 in RFPs. Treat the draft as a binding forward-looking signal—not current law—but one that shapes near-term tender criteria and vendor evaluations.
Initiate internal cross-functional alignment on data architecture and accessibility design
GDPR localisation and EN 301 549 V3.2.1 conformance are not post-manufacturing add-ons. Engineering, privacy, and UX teams must jointly review data flow diagrams, user interface code, assistive technology interfaces (e.g., WCAG-aligned ARIA labels), and default configuration settings. Early alignment reduces rework cycles and accelerates third-party assessment readiness.
Editorial Perspective / Industry Observation
Observably, this draft signals a structural shift in how the EU regulates digital infrastructure in shared physical spaces—not merely as IT equipment, but as regulated service delivery points with combined data protection and universal access obligations. Analysis shows the dual-certification mandate reflects growing policy convergence between digital rights (privacy, autonomy) and inclusive design (accessibility, usability). It is not yet an enforceable outcome, but rather a strong anticipatory signal: procurement gatekeepers and standards bodies are already aligning behind it. From an industry perspective, this is less about immediate compliance pressure and more about recalibrating product development roadmaps, supplier agreements, and tender response strategies over the next 12–18 months.

Conclusion
This draft regulation does not introduce new legal obligations overnight, but it crystallises an emerging compliance threshold for digital infrastructure serving EU public and hospitality environments. Its significance lies not in immediacy, but in directionality: it confirms that interoperability, data sovereignty, and accessibility are now co-equal pillars of market access. Enterprises are better advised to treat it as a forward-looking design and procurement benchmark—not a looming penalty trigger—and to calibrate investments accordingly.Source: European Commission draft proposal, Digital Services Infrastructure Compliance Amendment, published 23 May 2026. Status remains draft; final adoption and entry into force pending Member State consultation and potential revision. Ongoing monitoring required.
Recommended News
 Sep 08, 2026How to Build Stable Interoperability Across Hotel Guestroom SystemsHospitality system interoperability stable: learn how hotels can align room states, command priorities, local fallback, and testing for reliable guestroom operations.
 Aug 18, 2026What Hotel System Interoperability Means for PMS, POS, and Guestroom TechHotel system interoperability shapes how PMS, POS, and guestroom tech perform in real hotels. Learn the key risks, validation points, and smarter ways to build resilient operations.
 Aug 10, 2026How to Evaluate a Smart Hotel System Integration Quotation Before ApprovalSystem integration quotation for smart hotels: learn how to assess scope, interoperability, cybersecurity, lifecycle cost, and hidden risks before approval.
 Jul 28, 2026How to Evaluate a Smart Hotel Application for Guest Experience and Staff EfficiencySmart hotel application evaluation made practical: learn how to compare integrations, guest journey design, staff workflows, security, and total cost to choose a smarter hotel solution.
 Jul 12, 2026Premium Camping Q2 Up 19% as Europe Expands Guestroom AutomationPremium camping grew 19% in Q2 as Europe accelerates guestroom automation. Discover how Germany, France, and Switzerland are driving demand for smarter campsites.
 Jul 11, 2026System Integration Testing for Resorts: Key Steps Before Guestroom Tech Goes LiveSystem integration testing for resorts: discover the 6 essential pre-opening steps to prevent guestroom tech failures, reduce launch risk, and protect guest satisfaction.
 Jul 10, 2026Hospitality System Interoperability Buyer Guide: What to Check Before You BuyHospitality system interoperability buyer guide: learn what to verify before you buy, from APIs and device compatibility to security, scalability, hidden costs, and vendor risk.
 Jul 09, 2026CPSC advisory puts offline AI checks on hotel voice devicesCPSC advisory reshapes compliance for hotel voice devices with offline AI. Learn how FCC Part 15 checks, labeling, and shipment readiness may impact U.S. hotel projects.
 Jul 08, 2026CPSC Sets Offline AI Rule for Guestroom Voice ModulesCPSC Sets Offline AI Rule for Guestroom Voice Modules: learn how the 2026 U.S. update impacts compliance, imports, hotel tech sourcing, and recall risk for suppliers.
 Jul 07, 2026CPSC Sets Offline AI Bar for Hotel Voice DevicesCPSC sets a new offline AI bar for hotel voice devices. Learn how the 2026 guidance impacts guestroom automation, import checks, supplier compliance, and hotel procurement decisions.
![]() Jul 06, 2026CPSC Requires Offline AI in Guestroom Voice SystemsCPSC requires offline AI in guestroom voice systems starting Oct 1, 2026. Learn how this rule impacts Alexa/Google integrations, compliance, procurement, and U.S. market shipments.
 Jul 06, 2026How to Reduce Hospitality System Interoperability Latency Across PMS, POS, and IoTHospitality system interoperability latency affects guest experience, revenue accuracy, and IoT responsiveness. Learn practical ways to reduce delays across PMS, POS, and smart hotel systems.
 Jul 05, 2026CPSC Orders Offline AI for Hotel Voice ModulesCPSC orders offline AI for hotel voice modules by Oct 1, 2026. Learn how local AI inference rules will impact U.S. hotel automation sourcing, integration, and compliance.
 Jul 04, 2026CPSC Mandates Offline AI for Guestroom Voice UnitsCPSC mandates offline AI for guestroom voice units entering the U.S. Learn how FCC Part 15B and UL 60730-1 compliance will reshape hotel procurement, OEM design, and delivery plans.
 Jul 03, 2026CPSC Requires Offline AI for Guestroom Voice ModulesCPSC Requires Offline AI for Guestroom Voice Modules: learn what the emergency U.S. rule means for compliance, sourcing, hotel tech procurement, and avoiding delisting or fines.
 Jul 02, 2026CPSC Requires Offline AI for Hotel Voice DevicesCPSC Requires Offline AI for Hotel Voice Devices: learn how the new U.S. rule impacts hotel automation, OEM/ODM suppliers, and guestroom voice compliance.
 Jul 01, 2026CPSC Orders Offline Voice Processing for Hotel Room SystemsCPSC orders offline voice processing for hotel room systems, making cloud-based voice control a live compliance risk. Learn what manufacturers, exporters, and hotel buyers must review now.
 Jul 01, 2026System Integration Testing for Smart Buildings: What to Verify Before HandoverSystem integration testing smart building projects must verify interoperability, alarms, cybersecurity, and data quality before handover. Learn what to check for a safer, smoother launch.
 Jun 28, 2026UL Tightens Guestroom Automation Rules on AI Voice DataUL tightens Guestroom Automation rules on AI voice data from Oct. 1, 2026. Learn how UL 2900-3:2026 affects certification, product design, and U.S. export readiness.
 Jun 26, 2026Smart Hospitality in Southeast Asia: Which Guestroom Automation Features Matter Most?Smart hospitality Southeast Asia is reshaping hotel operations. Discover which guestroom automation features truly boost guest satisfaction, efficiency, and long-term asset value.
 Jun 23, 2026How Smart Hospitality Solutions Improve Check-In, Energy Control, and Guest ExperienceSmart hospitality solutions improve check-in speed, energy control, and guest experience by aligning automation with property type, occupancy patterns, and operational performance.
 Jun 22, 2026Germany Sets TR-03147 Rule for Guestroom AutomationGermany sets TR-03147 V2.1 rule for Guestroom Automation from Oct 1, 2026. Learn CE marking impacts, cybersecurity requirements, and what suppliers, buyers, and exporters must do now.
 Jun 21, 2026Germany Sets Mandatory Cybersecurity Certification for Guestroom AutomationGermany Sets Mandatory Cybersecurity Certification for Guestroom Automation: learn how TR-03163-2 rules from April 2027 will impact hotel tech vendors, integrators, and buyers in Germany.
 Jun 20, 2026Canada Ends Subsidy Probe Into CIMC Reefer UnitCanada Ends Subsidy Probe Into CIMC Reefer Unit: learn how the CBSA de minimis ruling may ease North American compliance, sourcing risk, and market access for certified high-efficiency equipment.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.