Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- What Engineering Performance Testing Should Cover During a Specification ReviewEngineering performance testing for specification review: learn how to verify structural strength, durability, safety, sustainability, and system reliability before costly project decisions.
- Planning Recreational Cable Transport Networks for Resorts and Mountain ParksExplore recreational cable transport networks for resorts and mountain parks, with expert planning insights on capacity, terrain, safety, station design, and long-term performance.
- How to Plan Theme Park Infrastructure for Mixed-Use DevelopmentsTheme park infrastructure for mixed use developments: plan resilient utilities, circulation, attractions, hospitality, and digital systems for scalable destinations.
Popular Tags
TerraVista Metrics (TVM)Industry NewsCPSC Launches COPPA 2.0 Review for Kiosk AI Interfaces
auth.Lydia Vancini (Smart Hospitality IoT Consultant)Time
Sep 03, 2026Click Count
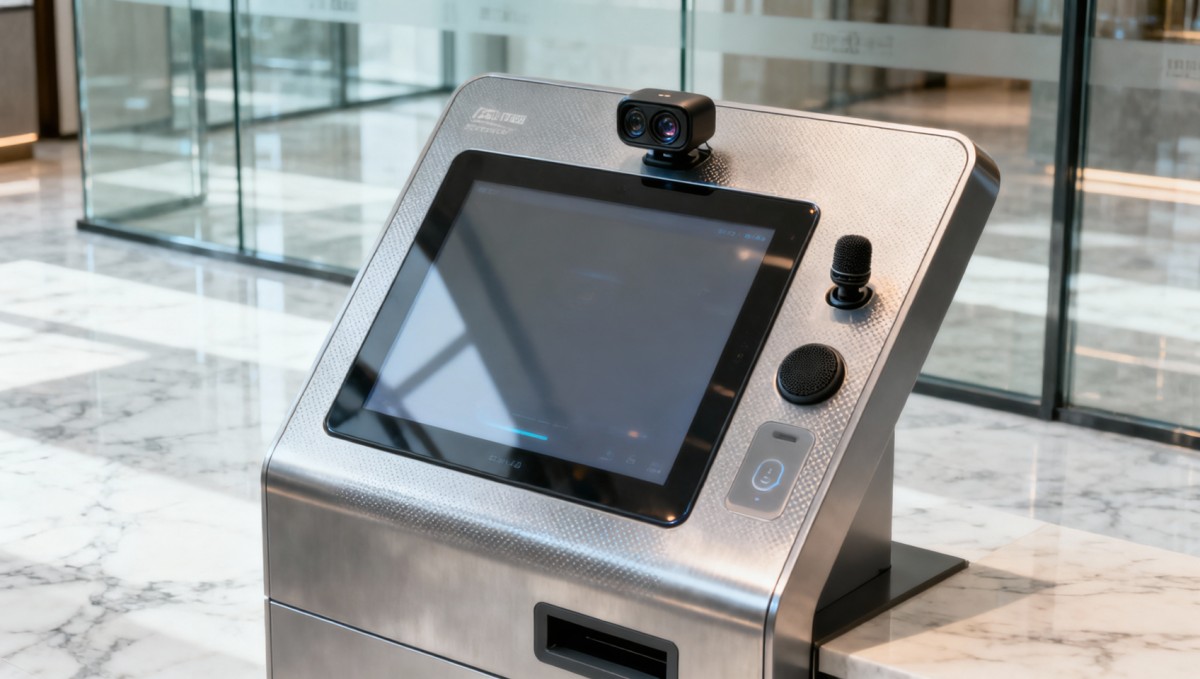
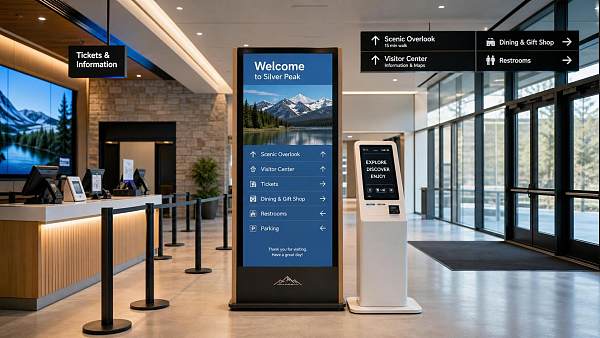
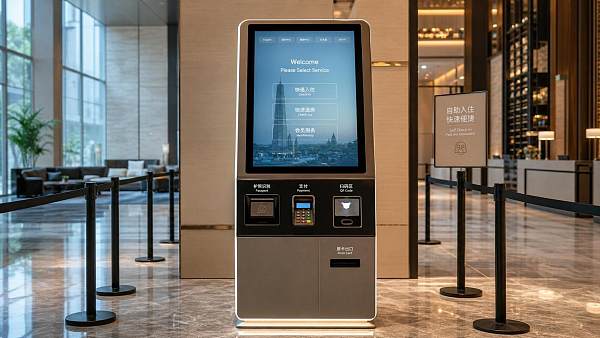
On May 1, 2026, the U.S. Consumer Product Safety Commission (CPSC) initiated a targeted compliance review—Kiosk Tech COPPA 2.0—focused on AI-driven interactive modules in public self-service terminals used by minors. This action directly affects manufacturers and operators of hotel check-in kiosks, tourist information displays, and retail guidance kiosks—particularly those exporting from China. It signals a tightening of cross-agency enforcement at the intersection of device safety, data privacy, and child protection.
Event Overview
On May 1, 2026, the U.S. Consumer Product Safety Commission (CPSC) announced the launch of the Kiosk Tech COPPA 2.0 Compliance Initiative. Under this initiative, all AI-powered voice and image interaction modules embedded in public self-service kiosks intended for use by children—including hotel check-in systems, scenic area guide screens, and retail product recommendation terminals—must concurrently obtain two certifications: FCC Part 15 radiofrequency compliance certification and FTC COPPA 2.0 child data minimization audit approval. Chinese manufacturers failing to meet both requirements face mandatory product removal from U.S. markets and potential financial penalties.
Industries Affected
Manufacturers of Public Self-Service Terminals
These companies are directly impacted because their products now require dual certification before market entry. The requirement applies specifically to AI interaction components—not just hardware or software architecture, but functional modules handling voice input, facial recognition, or real-time image analysis directed at minors. Impact includes extended time-to-market, increased third-party testing costs, and redesign pressure where legacy AI interfaces lack granular data handling controls.
Export-Oriented Electronics OEM/ODM Firms
OEM and ODM suppliers serving global brands must now validate that their AI subsystems—whether developed in-house or integrated from third parties—meet both FCC RF emission limits and FTC’s updated data collection thresholds for users under 13. Since COPPA 2.0 emphasizes ‘data minimization’ rather than mere consent, firms may need to reconfigure logging, storage, and transmission logic—even for edge-processing-only deployments.
Distribution and Channel Partners in U.S. Retail & Hospitality
U.S.-based kiosk deployers and system integrators face operational risk if installed units lack valid dual certification. CPSC’s enforcement scope includes post-deployment verification; non-compliant units identified during routine inspections—or via consumer complaints—may trigger recall notices or service suspension orders. This shifts liability upstream and increases due diligence obligations during procurement and maintenance cycles.
What Stakeholders Should Monitor and Do Now
Track official guidance from CPSC, FCC, and FTC on implementation timelines
The May 1, 2026 announcement marks the start of the review—not the effective date of enforcement. Stakeholders should monitor forthcoming FAQs, interpretive bulletins, and any phased rollout schedule issued jointly by the three agencies. No grace period has been publicly confirmed; however, historical precedent suggests notice-and-comment periods often precede full enforcement.
Verify certification status of AI modules—not just full kiosk units
Certification responsibility falls on the entity introducing the AI interface into commerce. Firms should confirm whether their AI stack (e.g., speech-to-text engine, age-estimation model, or gesture-recognition firmware) has undergone separate FCC Part 15 testing and FTC-aligned data flow mapping. Integrated solutions from vendors may not automatically inherit compliance across both regimes.
Distinguish between policy intent and enforceable requirements
COPPA 2.0 remains an evolving framework. While the CPSC’s action signals interagency alignment, FTC rulemaking on ‘data minimization’ standards for AI interfaces is still pending formal adoption. Current enforcement relies on existing COPPA principles interpreted through new technical contexts—not codified new rules. Companies should avoid over-engineering based on draft interpretations.
Initiate internal gap assessment for AI data handling and RF design documentation
Firms should compile existing test reports, data processing inventories, and firmware architecture diagrams related to minor-facing interactions. Prioritize documentation that links specific AI functions (e.g., ‘smile detection for user engagement’) to data collection points, retention durations, and transmission pathways—key inputs for FTC audit readiness.
Editorial Perspective / Industry Observation
Observably, this initiative reflects a structural shift: U.S. regulators are no longer treating interactive kiosks as passive hardware, but as data-collecting endpoints subject to layered jurisdiction. The pairing of FCC (device-level emissions) and FTC (behavioral data practices) signals convergence across traditionally siloed regulatory domains. Analysis shows this is less a finalized mandate and more a coordinated signal—designed to prompt industry self-audit ahead of formal rule updates. From an industry standpoint, it underscores growing expectations that AI functionality embedded in physical consumer products must satisfy both safety and privacy thresholds simultaneously—not sequentially.
Consequently, the current phase is best understood as a preparatory alignment window—not yet a compliance deadline with automatic penalties. However, given CPSC’s statutory authority to act on ‘imminent hazards’, early noncompliance could trigger case-specific interventions even before broader enforcement guidelines are published.

In summary, the CPSC’s Kiosk Tech COPPA 2.0 review establishes a new benchmark for AI-integrated public terminals targeting minors in the U.S. market. Its significance lies not only in added certification steps, but in the precedent it sets for multi-agency, function-specific oversight of embedded AI. For stakeholders, the immediate value is clarity on where regulatory scrutiny is converging—and how to prioritize technical and procedural adjustments accordingly.
Source: U.S. Consumer Product Safety Commission (CPSC) official announcement dated May 1, 2026. Note: FCC and FTC have not yet issued co-signed implementation guidance; ongoing monitoring is recommended.
Recommended News
 Aug 04, 2026What Tourism Hardware Does a Visitor Center Need for Better Wayfinding and Service?Tourism hardware for visitor centers: discover the essential signs, kiosks, counters, and queue systems that improve wayfinding, service efficiency, accessibility, and visitor experience.
 Jul 14, 2026West Coast Port Strain Extends Kiosk Tech Sea Lead TimesWest Coast port strain is extending Kiosk Tech sea lead times to 48 days, raising PSS and delivery risk. See what exporters, buyers, and service teams must do now.
 Jul 12, 2026US West Coast Strike Extends Kiosk Tech Lead TimesUS West Coast Strike Extends Kiosk Tech Lead Times—learn how port disruption, Red Sea rerouting, and Mexico diversion are reshaping Q3 inventory, routing, and delivery planning.
 Jul 12, 2026How to Compare Cost Effective Slide Systems for Kiosks, Cabinets, and Compact EquipmentCost effective slide systems compared for kiosks, cabinets, and compact equipment. Learn how to evaluate load, cycle life, fit, and maintenance for smarter sourcing.
 Jul 10, 2026GCC Rule Adds Local Privacy Sandbox to Facial Recognition KiosksGCC rule updates put facial recognition kiosks under tighter compliance from July 10, 2026. Learn how local privacy sandbox firmware, GSO reports, and longer lead times affect GCC market access.
 Jul 09, 2026Singapore Tightens Kiosk Imports for Facial RecognitionSingapore Tightens Kiosk Imports for Facial Recognition: learn the new PSB rules, firmware SDK, and local data caching requirements before August 1, 2026.
 Jul 08, 2026ISPO Munich Adds Smart Wayfinding Pavilion as EU-US Interest Jumps 67%ISPO Munich spotlights smart wayfinding as EU-US interest jumps 67%. Explore AR navigation, multilingual kiosks, and offline maps shaping outdoor venue projects.
 Jul 07, 2026ISPO 2026 Kiosk Zone Signals New Buying RulesISPO 2026 Kiosk Zone signals new buying rules for smart wayfinding terminals, highlighting EN 301 549 compliance, localized CMS needs, and rising EU buyer demand.
![]() Jul 06, 2026ISPO Adds Kiosk Tech as China Draws Buyer InterestISPO adds Kiosk Tech as China draws buyer interest, signaling rising demand for IP65 outdoor kiosk terminals, offline OTA maps, and multilingual guidance solutions for parks, resorts, and ski areas.
 Jul 06, 2026Resort Self Check-In Kiosks: Best Use Cases, Guest Flow Risks, and Setup TipsResort self check in kiosks explained: discover the best use cases, common guest flow risks, and practical setup tips to reduce queues and improve resort arrivals.
 Jul 05, 2026ISPO Munich 2026 Adds Kiosk Tech Zone as Chinese Outdoor Terminals Draw OrdersISPO Munich 2026 spotlights kiosk tech as Chinese outdoor terminals win 1,240 orders. Explore how smart wayfinding, AR navigation, and solar-powered kiosks are reshaping parks and resorts.
 Jul 04, 2026ISPO Opens Kiosk Tech Zone as China Devices Draw BuyersISPO Opens Kiosk Tech Zone as China devices draw buyers, highlighting demand for smart guide terminals with offline maps, AR, and LoRaWAN/NB-IoT—see what suppliers and buyers should prepare now.
 Jul 03, 2026ISPO Munich 2026 Debuts Kiosk Tech ZoneISPO Munich 2026 debuts Kiosk Tech Zone, spotlighting smart wayfinding kiosks for ski resorts. Explore buyer demand for IP65+, -30°C performance, AR navigation, and offline maps.
 Jul 02, 2026ISPO Adds Kiosk Tech Zone as China Suppliers Draw OrdersISPO adds Kiosk Tech Zone as China suppliers win orders for smart wayfinding kiosks. Explore how IP66, solar charging, offline maps, and rising MOQs are reshaping procurement.
 Jul 01, 2026ISPO Munich 2026 Adds Kiosk Tech as Chinese Guide Terminals Draw BuyersISPO Munich 2026 spotlights Kiosk Tech as Chinese guide terminals attract buyers with multilingual AR navigation and offline maps. Explore the 210% order surge, delivery timelines, and GDPR-ready deployment trends.
 Jul 01, 2026Kiosk Technology for Guest Services: Which Features Improve Check-In and Self-ServiceKiosk technology for guest services: discover which features improve check-in, self-service speed, system integration, and guest satisfaction across hotels, resorts, and attractions.
 Jun 30, 2026SASO Opens 72-Hour Fast Track for Kiosk TechSASO Opens 72-Hour Fast Track for Kiosk Tech: learn how Saudi local cloud hosting, ISO/IEC 27001:2022, and FastTrack-3 can cut approval time and speed market entry.
 Jun 29, 2026Saudi SASO Tightens Kiosk Cloud Hosting RulesSaudi SASO Tightens Kiosk Cloud Hosting Rules: learn how the 2026 SABER update affects smart kiosk compliance, local cloud hosting, certification, and Saudi market entry.
 Jun 25, 2026Tongcheng Links to WeChat AI Ecosystem for Kiosk ExpansionTongcheng Links to WeChat AI Ecosystem for Kiosk Expansion: explore how multilingual voice, AR wayfinding, and offline facial verification could reshape airport kiosks and cross-border travel tech.
 Jun 12, 2026China Ticketing Probe Raises Kiosk Compliance FocusChina Ticketing Probe raises urgent Kiosk Tech compliance questions for RV Components suppliers, from biometric data controls to GDPR and China PIPL readiness across global deployments.
 Jun 01, 2026New Zealand Border Fee Hits Kiosk Tech ShippingNew Zealand border fee adds NZD 12.50 to low-value kiosk tech shipping. See how importers can manage costs, customs planning, and delivery timelines.
 May 23, 2026EU to Revise Cybersecurity Act: Data Localization Pressure Rises for Kiosk Tech & Guestroom AutomationEU Cybersecurity Act revision mandates data localization & EN 303 645:2025 certification for kiosk tech and guestroom automation—act now to secure EU market access.
 May 22, 2026Vietnam TISI Launches Fast-Track for Kiosk Tech Under GB/T 35658-2025Vietnam TISI’s new fast-track certification for kiosk tech under GB/T 35658-2025 slashes approval to 12 days — boost B2G exports & win public sector tenders faster.
 May 22, 2026When a smart hotel mobile app helps more than self check inSmart hotel mobile app value goes far beyond self check in—discover how it improves security, service workflows, IoT control, and hotel efficiency with a practical evaluation checklist.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.