Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- How to Evaluate Spark Plug Suppliers for Consistent Quality and Lead TimesSpark plugs supplier evaluation guide: compare quality control, traceability, fitment, total cost, and reliable lead times to secure dependable engine maintenance supply.
- What Drives System Interoperability Testing Service Costs in Complex Projects?System interoperability testing service cost depends on integration scope, workflows, environments, and assurance needs. Learn how to budget smarter and reduce project risk.
- Project Planning Sourcing Guides: How to Qualify Suppliers Before Work StartsSourcing guides project planning helps teams qualify suppliers before work begins—verify compliance, delivery capacity, financial strength, and sustainability to reduce risk and protect project outcomes.
Popular Tags
TerraVista Metrics (TVM)Industry NewsVietnam TISI Expands Data Sandbox Exemption for Kiosk Tech
auth.Lydia Vancini (Smart Hospitality IoT Consultant)Time
Oct 07, 2026Click Count
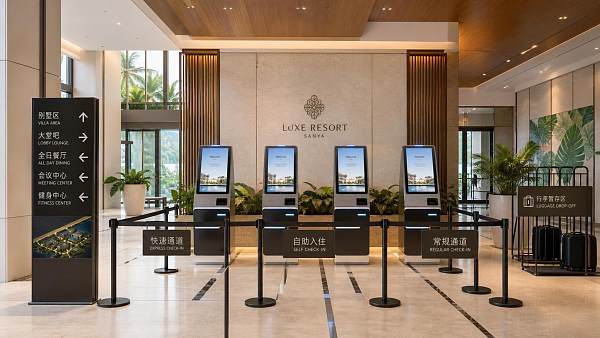
On May 11, 2026, Vietnam’s Institute of Standards and Industrial Research (TISI) updated its Implementation Rules on Data Localization for Kiosk Technology, introducing a data sandbox exemption for Sino-Vietnamese joint entities holding both China’s CCRC Level 3 (or higher) and Vietnam’s VNCERT Level 2 certifications. This development directly affects enterprises in smart cultural tourism, hospitality digital services, and self-service terminal deployment—particularly those operating or supplying kiosks for scenic area guidance and hotel check-in systems.
Event Overview
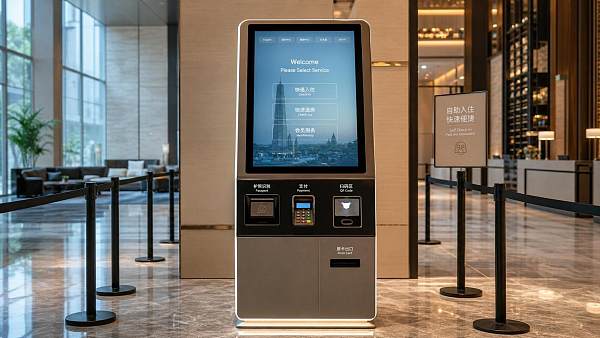
On May 11, 2026, the Vietnam Institute of Standards and Industrial Research (TISI) issued an update to the Kiosk Tech Data Localization Implementation Rules. Under the revised rules, Sino-Vietnamese joint entities that hold both China’s Cybersecurity Capacity Evaluation Certification (CCRC) at Level 3 or above and Vietnam’s National Center for Information Security Certification (VNCERT) at Level 2 are fully exempted from mandatory pre-export sandbox simulation testing for user behavior data. The policy took effect immediately and applies specifically to smart cultural tourism guide terminals and hotel self-check-in kiosks.
Industries Affected by This Policy Change
Channel Distributors in Vietnam
Channel distributors—including local system integrators, hospitality technology resellers, and tourism infrastructure providers—are directly impacted because the exemption eliminates the average 45-day data compliance lead time previously required before deploying kiosk solutions. Their ability to accelerate project timelines depends on partnering with qualified Chinese solution providers holding the dual certification.
Chinese Solution Providers (Hardware + Software Integrators)
Chinese vendors offering end-to-end kiosk systems—including hardware OEMs, firmware developers, and cloud-based service platforms—face new market access conditions. Without both CCRC Level 3+ and VNCERT Level 2, they cannot qualify for the exemption, limiting their competitiveness in time-sensitive Vietnamese deployments.
Joint Venture & Consortium Operators
Entities structured as formal Sino-Vietnamese joint ventures—or certified consortiums registered under applicable Vietnamese commercial law—are the only operational models explicitly recognized under the exemption. Standalone foreign subsidiaries or informal partnerships do not qualify, even if technically compliant.
What Relevant Enterprises or Practitioners Should Focus On
Monitor official TISI guidance on dual-certification verification procedures
While the exemption is effective, TISI has not yet published detailed criteria for validating joint entity status or cross-recognition of CCRC/VNCERT credentials. Enterprises should track TISI’s forthcoming technical notices or FAQs—especially regarding documentation requirements for consortium registration and certificate submission formats.
Confirm eligibility of existing or planned kiosk deployments
The exemption applies only to devices used in smart cultural tourism guidance and hotel self-check-in contexts. It does not extend to other kiosk applications (e.g., banking, government services, retail). Companies must verify whether their current or planned product scope falls within the defined use cases before assuming applicability.
Distinguish between regulatory signal and immediate operational readiness
Analysis shows this exemption reflects TISI’s prioritization of interoperability and trusted bilateral certification frameworks—but it does not replace broader Vietnamese data protection obligations under Decree 13/2023/ND-CP. Entities remain responsible for lawful data collection, storage, and processing; the sandbox waiver applies solely to outbound simulation testing for user behavior data.
Prepare documentation and alignment with Vietnamese partners early
Because joint entity qualification requires coordinated certification maintenance, Chinese suppliers should initiate alignment with Vietnamese partners on documentation workflows—including bilingual audit reports, certificate validity windows, and renewal coordination cycles—well ahead of project tendering or contract signing.
Editorial Perspective / Industry Observation
Observably, this update functions less as a broad deregulatory shift and more as a targeted facilitation mechanism for vetted, certifiably secure cross-border tech delivery. From an industry perspective, it signals growing institutional recognition of aligned cybersecurity evaluation standards between China and Vietnam—but only within narrowly defined technical and operational boundaries. Current implementation remains contingent on verifiable joint certification status and strict use-case alignment. Therefore, the policy is better understood as an operational enabler for specific projects rather than a structural easing of Vietnam’s data localization regime.
In summary, this TISI update introduces a concrete, conditional pathway to accelerate kiosk deployment in Vietnam’s tourism and hospitality sectors—yet its utility is tightly bound to certification rigor, joint-entity structure, and precise functional scope. It does not represent a general relaxation of data governance requirements, nor does it extend to adjacent verticals or uncertified actors. For stakeholders, the most pragmatic interpretation is that it lowers one procedural barrier—not a systemic one—and only for those already positioned within the dual-certification framework.
Source: Official announcement by Vietnam Institute of Standards and Industrial Research (TISI), dated May 11, 2026; referenced document: Implementation Rules on Data Localization for Kiosk Technology (revised edition). Note: Verification procedures for dual certification and consortium validation remain pending formal publication and are subject to ongoing observation.
Recommended News
 Aug 04, 2026What Tourism Hardware Does a Visitor Center Need for Better Wayfinding and Service?Tourism hardware for visitor centers: discover the essential signs, kiosks, counters, and queue systems that improve wayfinding, service efficiency, accessibility, and visitor experience.
 Jul 14, 2026West Coast Port Strain Extends Kiosk Tech Sea Lead TimesWest Coast port strain is extending Kiosk Tech sea lead times to 48 days, raising PSS and delivery risk. See what exporters, buyers, and service teams must do now.
 Jul 12, 2026US West Coast Strike Extends Kiosk Tech Lead TimesUS West Coast Strike Extends Kiosk Tech Lead Times—learn how port disruption, Red Sea rerouting, and Mexico diversion are reshaping Q3 inventory, routing, and delivery planning.
 Jul 12, 2026How to Compare Cost Effective Slide Systems for Kiosks, Cabinets, and Compact EquipmentCost effective slide systems compared for kiosks, cabinets, and compact equipment. Learn how to evaluate load, cycle life, fit, and maintenance for smarter sourcing.
 Jul 10, 2026GCC Rule Adds Local Privacy Sandbox to Facial Recognition KiosksGCC rule updates put facial recognition kiosks under tighter compliance from July 10, 2026. Learn how local privacy sandbox firmware, GSO reports, and longer lead times affect GCC market access.
 Jul 09, 2026Singapore Tightens Kiosk Imports for Facial RecognitionSingapore Tightens Kiosk Imports for Facial Recognition: learn the new PSB rules, firmware SDK, and local data caching requirements before August 1, 2026.
 Jul 08, 2026ISPO Munich Adds Smart Wayfinding Pavilion as EU-US Interest Jumps 67%ISPO Munich spotlights smart wayfinding as EU-US interest jumps 67%. Explore AR navigation, multilingual kiosks, and offline maps shaping outdoor venue projects.
 Jul 07, 2026ISPO 2026 Kiosk Zone Signals New Buying RulesISPO 2026 Kiosk Zone signals new buying rules for smart wayfinding terminals, highlighting EN 301 549 compliance, localized CMS needs, and rising EU buyer demand.
![]() Jul 06, 2026ISPO Adds Kiosk Tech as China Draws Buyer InterestISPO adds Kiosk Tech as China draws buyer interest, signaling rising demand for IP65 outdoor kiosk terminals, offline OTA maps, and multilingual guidance solutions for parks, resorts, and ski areas.
 Jul 06, 2026Resort Self Check-In Kiosks: Best Use Cases, Guest Flow Risks, and Setup TipsResort self check in kiosks explained: discover the best use cases, common guest flow risks, and practical setup tips to reduce queues and improve resort arrivals.
 Jul 05, 2026ISPO Munich 2026 Adds Kiosk Tech Zone as Chinese Outdoor Terminals Draw OrdersISPO Munich 2026 spotlights kiosk tech as Chinese outdoor terminals win 1,240 orders. Explore how smart wayfinding, AR navigation, and solar-powered kiosks are reshaping parks and resorts.
 Jul 04, 2026ISPO Opens Kiosk Tech Zone as China Devices Draw BuyersISPO Opens Kiosk Tech Zone as China devices draw buyers, highlighting demand for smart guide terminals with offline maps, AR, and LoRaWAN/NB-IoT—see what suppliers and buyers should prepare now.
 Jul 03, 2026ISPO Munich 2026 Debuts Kiosk Tech ZoneISPO Munich 2026 debuts Kiosk Tech Zone, spotlighting smart wayfinding kiosks for ski resorts. Explore buyer demand for IP65+, -30°C performance, AR navigation, and offline maps.
 Jul 02, 2026ISPO Adds Kiosk Tech Zone as China Suppliers Draw OrdersISPO adds Kiosk Tech Zone as China suppliers win orders for smart wayfinding kiosks. Explore how IP66, solar charging, offline maps, and rising MOQs are reshaping procurement.
 Jul 01, 2026ISPO Munich 2026 Adds Kiosk Tech as Chinese Guide Terminals Draw BuyersISPO Munich 2026 spotlights Kiosk Tech as Chinese guide terminals attract buyers with multilingual AR navigation and offline maps. Explore the 210% order surge, delivery timelines, and GDPR-ready deployment trends.
 Jul 01, 2026Kiosk Technology for Guest Services: Which Features Improve Check-In and Self-ServiceKiosk technology for guest services: discover which features improve check-in, self-service speed, system integration, and guest satisfaction across hotels, resorts, and attractions.
 Jun 30, 2026SASO Opens 72-Hour Fast Track for Kiosk TechSASO Opens 72-Hour Fast Track for Kiosk Tech: learn how Saudi local cloud hosting, ISO/IEC 27001:2022, and FastTrack-3 can cut approval time and speed market entry.
 Jun 29, 2026Saudi SASO Tightens Kiosk Cloud Hosting RulesSaudi SASO Tightens Kiosk Cloud Hosting Rules: learn how the 2026 SABER update affects smart kiosk compliance, local cloud hosting, certification, and Saudi market entry.
 Jun 25, 2026Tongcheng Links to WeChat AI Ecosystem for Kiosk ExpansionTongcheng Links to WeChat AI Ecosystem for Kiosk Expansion: explore how multilingual voice, AR wayfinding, and offline facial verification could reshape airport kiosks and cross-border travel tech.
 Jun 12, 2026China Ticketing Probe Raises Kiosk Compliance FocusChina Ticketing Probe raises urgent Kiosk Tech compliance questions for RV Components suppliers, from biometric data controls to GDPR and China PIPL readiness across global deployments.
 Jun 01, 2026New Zealand Border Fee Hits Kiosk Tech ShippingNew Zealand border fee adds NZD 12.50 to low-value kiosk tech shipping. See how importers can manage costs, customs planning, and delivery timelines.
 May 23, 2026EU to Revise Cybersecurity Act: Data Localization Pressure Rises for Kiosk Tech & Guestroom AutomationEU Cybersecurity Act revision mandates data localization & EN 303 645:2025 certification for kiosk tech and guestroom automation—act now to secure EU market access.
 May 22, 2026Vietnam TISI Launches Fast-Track for Kiosk Tech Under GB/T 35658-2025Vietnam TISI’s new fast-track certification for kiosk tech under GB/T 35658-2025 slashes approval to 12 days — boost B2G exports & win public sector tenders faster.
 May 22, 2026When a smart hotel mobile app helps more than self check inSmart hotel mobile app value goes far beyond self check in—discover how it improves security, service workflows, IoT control, and hotel efficiency with a practical evaluation checklist.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.