Search News
TerraVista Metrics (TVM)Industry Portal
TerraVista Metrics (TVM)Hot Articles
TerraVista Metrics (TVM)- What Drives System Interoperability Testing Service Costs in Complex Projects?System interoperability testing service cost depends on integration scope, workflows, environments, and assurance needs. Learn how to budget smarter and reduce project risk.
- Project Planning Sourcing Guides: How to Qualify Suppliers Before Work StartsSourcing guides project planning helps teams qualify suppliers before work begins—verify compliance, delivery capacity, financial strength, and sustainability to reduce risk and protect project outcomes.
- Buyer’s Guide to Kinetic Art: Choosing Safe, Durable Pieces for Public SpacesBuyer guides kinetic art for public spaces: learn how to choose safe, durable, low-maintenance installations with reliable engineering, materials, controls, and lifecycle value.
Popular Tags
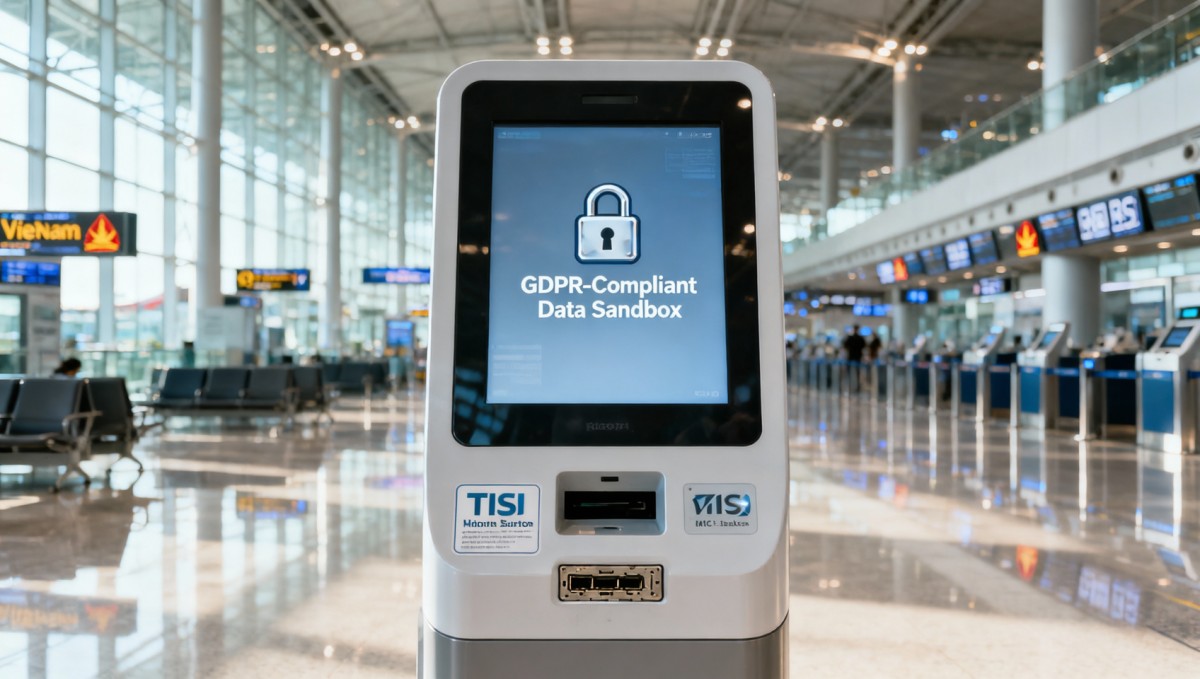
TerraVista Metrics (TVM)Industry NewsVietnam TISI Updates Kiosk Import Rules: Local GDPR-Compliant Data Sandbox Required
auth.Lydia Vancini (Smart Hospitality IoT Consultant)Time
Oct 06, 2026Click Count
Vietnam’s General Department of Standards, Metrology and Quality (TISI) issued Circular 18/2026/TT-BKHCN on May 3, 2026, mandating that all imported kiosk technology devices—including hotel self-check-in terminals, tourist information kiosks, and duty-free payment亭—must embed a locally certified data sandbox before market entry. This development directly affects cross-border hardware exporters, system integrators, and digital service providers operating in Vietnam’s smart infrastructure and retail-tech sectors.
Event Overview
On May 3, 2026, Vietnam’s Ministry of Science and Technology published Circular 18/2026/TT-BKHCN through the General Department of Standards, Metrology and Quality (TISI). The circular requires all kiosk tech devices entering Vietnam—including hotel self-check-in kiosks, scenic area guidance terminals, and duty-free store payment kiosks—to be pre-installed with a ‘local data sandbox’ certified by the Ministry of Information and Communications (MIC). This sandbox must ensure encrypted, onshore isolation of sensitive user data—including biometric identifiers, payment records, and location trajectories—and comply with GDPR Articles 44–49 regarding international data transfers. Chinese kiosk manufacturers must integrate this module at the firmware level to obtain import clearance.
Which Subsectors Are Affected
Hardware Exporters (especially from China)
Exporters supplying kiosk devices to Vietnam must now redesign firmware architecture to embed MIC-certified sandbox logic prior to shipment. Non-compliant units will be denied customs clearance, triggering delays, rework costs, or rejection at port.
System Integrators & Solution Providers
Firms deploying end-to-end kiosk solutions—including software customization, cloud connectivity, and backend integration—face new certification dependencies. Their deployment timelines now hinge on verified sandbox compatibility, not just functional testing.
Payment & Identity Verification Tech Suppliers
Vendors providing biometric modules, EMV payment stacks, or location-aware SDKs must confirm interoperability with the mandated sandbox environment. Any third-party component handling sensitive data may require revalidation under the new framework.
Duty-Free Retailers & Hospitality Operators
End users procuring kiosks for Vietnamese locations face extended procurement cycles and higher upfront validation requirements. Procurement contracts must now include clauses covering sandbox compliance, firmware audit rights, and post-deployment certification support.
What Enterprises and Practitioners Should Monitor and Do Now
Track official MIC sandbox certification criteria and approved vendors
The circular references MIC certification but does not publish technical specifications or a list of authorized sandbox implementations. Companies should monitor MIC’s official portal for updated guidance, as certification readiness—not just device readiness—will determine import eligibility.
Review firmware architecture and third-party SDK dependencies
Manufacturers must assess whether their current firmware supports secure enclave integration, encrypted local storage, and GDPR-aligned data flow controls. Dependencies on non-Vietnam-certified identity or payment libraries may necessitate substitution or co-certification.
Distinguish between policy issuance and operational enforcement
While Circular 18/2026/TT-BKHCN is effective upon publication, enforcement timelines—including grace periods, transitional arrangements, or phased implementation—are not specified. Observably, early enforcement may focus on high-visibility deployments (e.g., airports, major resorts), not small-scale pilots.
Prepare documentation for customs and MIC audits
Importers should begin compiling evidence of sandbox integration—including firmware version logs, encryption key management protocols, and data residency architecture diagrams—to meet potential requests during customs inspection or post-import verification.
Editorial Perspective / Industry Observation
This regulation is better understood as a signal of Vietnam’s accelerating alignment with EU-style data sovereignty frameworks—not merely a technical import requirement. Analysis shows it reflects broader national priorities around data localization, digital infrastructure control, and regulatory harmonization with global privacy standards. It is not yet a fully matured enforcement regime; rather, it marks the formal institutionalization of data residency as a gatekeeping condition for physical hardware imports. From an industry perspective, this signals growing convergence between cybersecurity policy, trade compliance, and embedded systems design—making cross-functional coordination (legal, firmware engineering, supply chain) essential for market access.
Conclusion
This circular establishes a new baseline for hardware market access in Vietnam—not as an isolated compliance hurdle, but as part of an evolving data governance infrastructure. Its immediate impact lies in shifting responsibility upstream: from end-user operators to device manufacturers and firmware developers. Currently, it is more accurately interpreted as a structural prerequisite than a finalized operational standard; its real-world impact will depend on MIC’s certification roadmap and enforcement consistency over the coming months.
Source Attribution
Main source: Vietnam Ministry of Science and Technology, Circular 18/2026/TT-BKHCN, issued May 3, 2026, published via TISI (General Department of Standards, Metrology and Quality).
Points requiring ongoing observation: MIC’s official sandbox certification criteria, list of authorized implementations, and any announced transition period or enforcement schedule.Recommended News
 Aug 04, 2026What Tourism Hardware Does a Visitor Center Need for Better Wayfinding and Service?Tourism hardware for visitor centers: discover the essential signs, kiosks, counters, and queue systems that improve wayfinding, service efficiency, accessibility, and visitor experience.
 Jul 14, 2026West Coast Port Strain Extends Kiosk Tech Sea Lead TimesWest Coast port strain is extending Kiosk Tech sea lead times to 48 days, raising PSS and delivery risk. See what exporters, buyers, and service teams must do now.
 Jul 12, 2026US West Coast Strike Extends Kiosk Tech Lead TimesUS West Coast Strike Extends Kiosk Tech Lead Times—learn how port disruption, Red Sea rerouting, and Mexico diversion are reshaping Q3 inventory, routing, and delivery planning.
 Jul 12, 2026How to Compare Cost Effective Slide Systems for Kiosks, Cabinets, and Compact EquipmentCost effective slide systems compared for kiosks, cabinets, and compact equipment. Learn how to evaluate load, cycle life, fit, and maintenance for smarter sourcing.
 Jul 10, 2026GCC Rule Adds Local Privacy Sandbox to Facial Recognition KiosksGCC rule updates put facial recognition kiosks under tighter compliance from July 10, 2026. Learn how local privacy sandbox firmware, GSO reports, and longer lead times affect GCC market access.
 Jul 09, 2026Singapore Tightens Kiosk Imports for Facial RecognitionSingapore Tightens Kiosk Imports for Facial Recognition: learn the new PSB rules, firmware SDK, and local data caching requirements before August 1, 2026.
 Jul 08, 2026ISPO Munich Adds Smart Wayfinding Pavilion as EU-US Interest Jumps 67%ISPO Munich spotlights smart wayfinding as EU-US interest jumps 67%. Explore AR navigation, multilingual kiosks, and offline maps shaping outdoor venue projects.
 Jul 07, 2026ISPO 2026 Kiosk Zone Signals New Buying RulesISPO 2026 Kiosk Zone signals new buying rules for smart wayfinding terminals, highlighting EN 301 549 compliance, localized CMS needs, and rising EU buyer demand.
![]() Jul 06, 2026ISPO Adds Kiosk Tech as China Draws Buyer InterestISPO adds Kiosk Tech as China draws buyer interest, signaling rising demand for IP65 outdoor kiosk terminals, offline OTA maps, and multilingual guidance solutions for parks, resorts, and ski areas.
 Jul 06, 2026Resort Self Check-In Kiosks: Best Use Cases, Guest Flow Risks, and Setup TipsResort self check in kiosks explained: discover the best use cases, common guest flow risks, and practical setup tips to reduce queues and improve resort arrivals.
 Jul 05, 2026ISPO Munich 2026 Adds Kiosk Tech Zone as Chinese Outdoor Terminals Draw OrdersISPO Munich 2026 spotlights kiosk tech as Chinese outdoor terminals win 1,240 orders. Explore how smart wayfinding, AR navigation, and solar-powered kiosks are reshaping parks and resorts.
 Jul 04, 2026ISPO Opens Kiosk Tech Zone as China Devices Draw BuyersISPO Opens Kiosk Tech Zone as China devices draw buyers, highlighting demand for smart guide terminals with offline maps, AR, and LoRaWAN/NB-IoT—see what suppliers and buyers should prepare now.
 Jul 03, 2026ISPO Munich 2026 Debuts Kiosk Tech ZoneISPO Munich 2026 debuts Kiosk Tech Zone, spotlighting smart wayfinding kiosks for ski resorts. Explore buyer demand for IP65+, -30°C performance, AR navigation, and offline maps.
 Jul 02, 2026ISPO Adds Kiosk Tech Zone as China Suppliers Draw OrdersISPO adds Kiosk Tech Zone as China suppliers win orders for smart wayfinding kiosks. Explore how IP66, solar charging, offline maps, and rising MOQs are reshaping procurement.
 Jul 01, 2026ISPO Munich 2026 Adds Kiosk Tech as Chinese Guide Terminals Draw BuyersISPO Munich 2026 spotlights Kiosk Tech as Chinese guide terminals attract buyers with multilingual AR navigation and offline maps. Explore the 210% order surge, delivery timelines, and GDPR-ready deployment trends.
 Jul 01, 2026Kiosk Technology for Guest Services: Which Features Improve Check-In and Self-ServiceKiosk technology for guest services: discover which features improve check-in, self-service speed, system integration, and guest satisfaction across hotels, resorts, and attractions.
 Jun 30, 2026SASO Opens 72-Hour Fast Track for Kiosk TechSASO Opens 72-Hour Fast Track for Kiosk Tech: learn how Saudi local cloud hosting, ISO/IEC 27001:2022, and FastTrack-3 can cut approval time and speed market entry.
 Jun 29, 2026Saudi SASO Tightens Kiosk Cloud Hosting RulesSaudi SASO Tightens Kiosk Cloud Hosting Rules: learn how the 2026 SABER update affects smart kiosk compliance, local cloud hosting, certification, and Saudi market entry.
 Jun 25, 2026Tongcheng Links to WeChat AI Ecosystem for Kiosk ExpansionTongcheng Links to WeChat AI Ecosystem for Kiosk Expansion: explore how multilingual voice, AR wayfinding, and offline facial verification could reshape airport kiosks and cross-border travel tech.
 Jun 12, 2026China Ticketing Probe Raises Kiosk Compliance FocusChina Ticketing Probe raises urgent Kiosk Tech compliance questions for RV Components suppliers, from biometric data controls to GDPR and China PIPL readiness across global deployments.
 Jun 01, 2026New Zealand Border Fee Hits Kiosk Tech ShippingNew Zealand border fee adds NZD 12.50 to low-value kiosk tech shipping. See how importers can manage costs, customs planning, and delivery timelines.
 May 23, 2026EU to Revise Cybersecurity Act: Data Localization Pressure Rises for Kiosk Tech & Guestroom AutomationEU Cybersecurity Act revision mandates data localization & EN 303 645:2025 certification for kiosk tech and guestroom automation—act now to secure EU market access.
 May 22, 2026Vietnam TISI Launches Fast-Track for Kiosk Tech Under GB/T 35658-2025Vietnam TISI’s new fast-track certification for kiosk tech under GB/T 35658-2025 slashes approval to 12 days — boost B2G exports & win public sector tenders faster.
 May 22, 2026When a smart hotel mobile app helps more than self check inSmart hotel mobile app value goes far beyond self check in—discover how it improves security, service workflows, IoT control, and hotel efficiency with a practical evaluation checklist.
Quarterly Executive Summaries Delivered Directly.
Join 50,000+ industry leaders who receive our proprietary market analysis and policy outlooks before they hit the public library.